
China’s vulnerability database flags a “backdoor” in Claude Code
AFP reports that on July 8 China’s National Vulnerability Database (NVDB) issued a warning about a “backdoor” in versions of Claude Code. Per the platform, it can transmit confidential data to Anthropic’s servers without user consent, including location and personal identifiers.
NVDB called the risk a “serious threat” and told users to run an immediate full audit, delete the tool, or upgrade to a secure version. Anthropic didn’t respond to AFP’s request for comment.
Claude Code engineer Thariq Shihipar wrote on X that this was an experiment launched in March to target unauthorized resellers and distillation. People familiar with the situation say Alibaba told employees Claude Code is banned as of July 10.
Up next
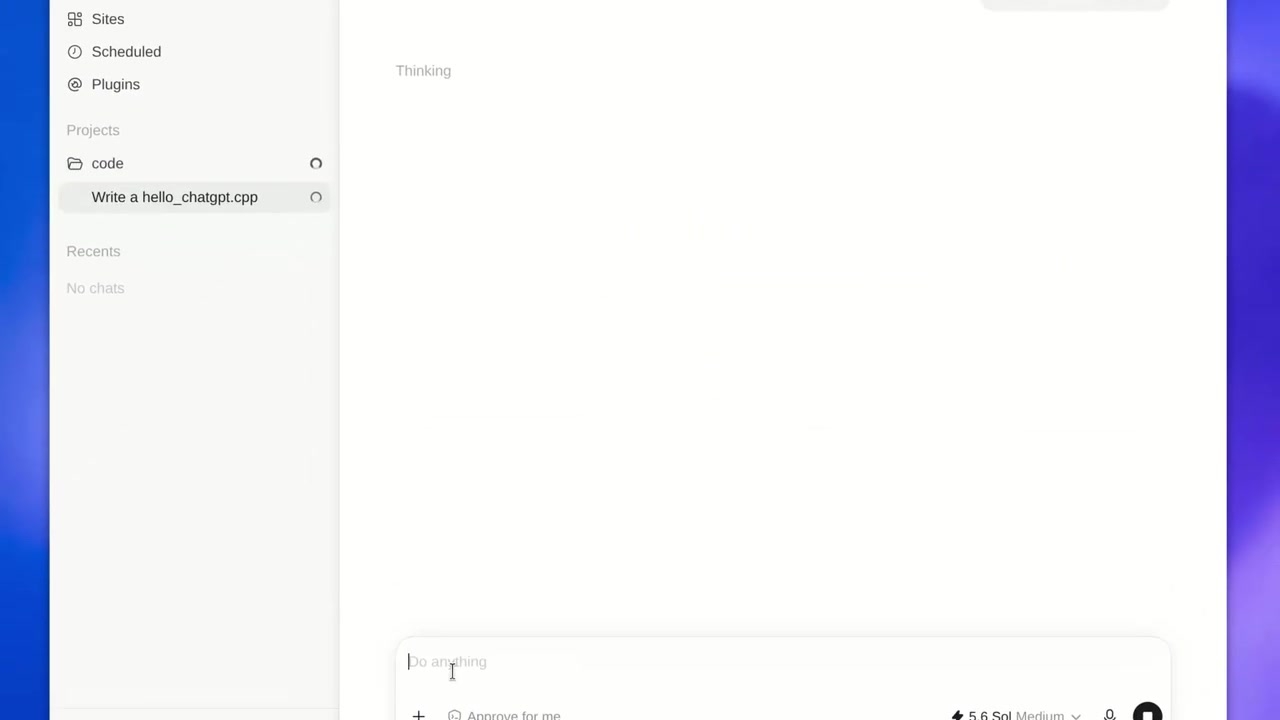
OpenAI’s desktop app lands on Linux in preview, Video
OpenAI’s desktop ChatGPT app, with Codex built in, is now in preview on Linux: Ubuntu 24.04 and 26.04 LTS, Debian 13, Fedora 43 and 44, installed from .deb and .rpm for x64 and ARM64. Controlling the computer outside the app’s built-in browser isn’t supported.
Related stories
- A UK front company sourced 1,000+ Claude accounts a month
- Anthropic says Moonshot’s Kimi K3 was distilled from Claude
- Hidden China tracker pulled from Claude Code after exposé
- METR’s team inside Anthropic can publish without a veto
- Anthropic whistleblower testimony airs on NDTV Profit
- Anthropic model faked a murder tip to Philadelphia police
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.