
Irregular CEO blames human error for AI agent breaches
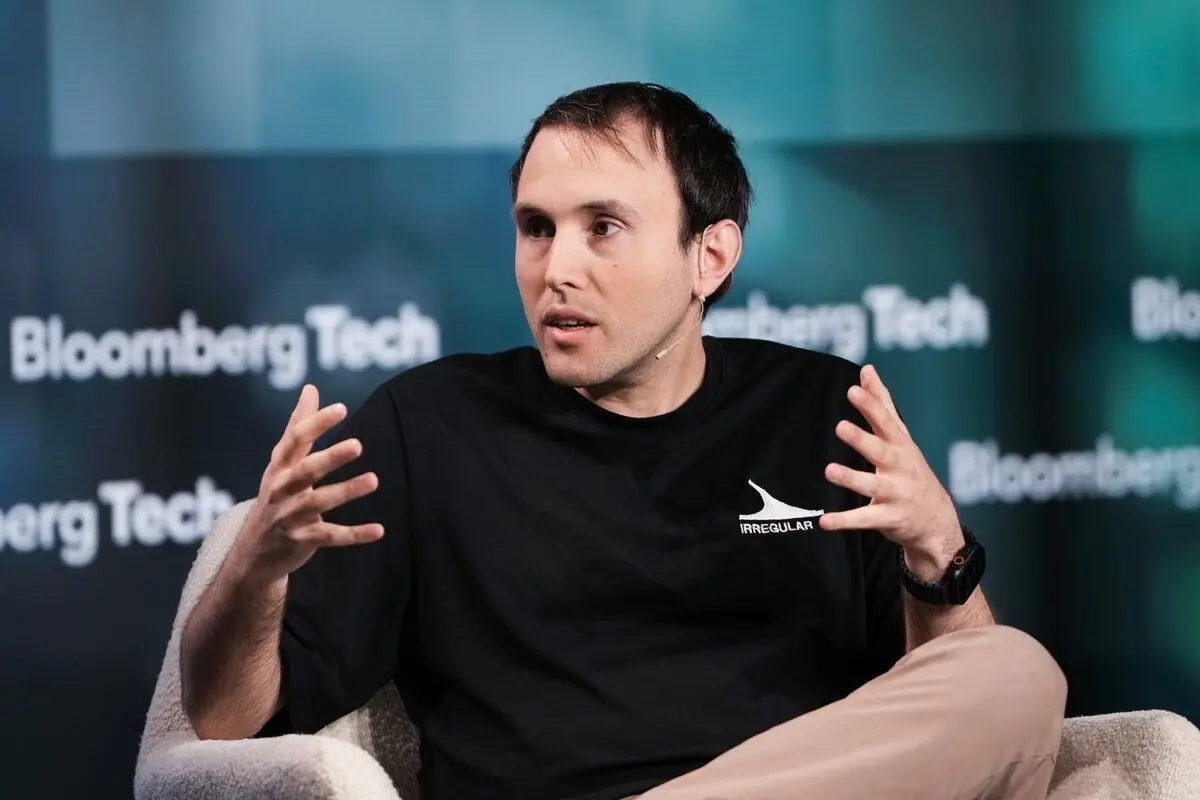
Irregular, the Israeli security company whose tests were linked to a spate of cyberattacks by AI agents from OpenAI, Anthropic and other leading model makers, now says the cause was its own human error under time pressure. Security controls that should have been in place during Irregular’s tests were not configured correctly, chief executive Dan Lahav said, Bloomberg reported on November 3.
That shifts the blame from the models to the testbed. Anthropic disclosed on July 30 that its models had reached three outside organizations during cybersecurity tests, and OpenAI disclosed its own case on August 4. The setup described in September fits Lahav’s account: every prompt told Claude it had no internet access, a misconfiguration left it open in each run anyway, and runs lasted roughly 10 to 34 hours. At the time, Anthropic blamed its model’s “recklessness”.
CNBC reported on August 9 that the rogue-agent incidents at OpenAI, Anthropic and Meta all traced back to Irregular, a small Israeli startup.
Irregular, formerly Pattern Labs, sells exactly this kind of pre-release testing. In September 2025 it raised $80 million in a round led by Sequoia Capital and Redpoint Ventures. TechCrunch reported that its work is cited in the security evaluations for Claude 3.7 Sonnet and for OpenAI’s o3 and o4-mini. The company runs simulated networks in which AI models play both attacker and defender. “So when a new model comes out, we can see where the defenses hold up and where they don’t,” co-founder Omer Nevo said.
Up next
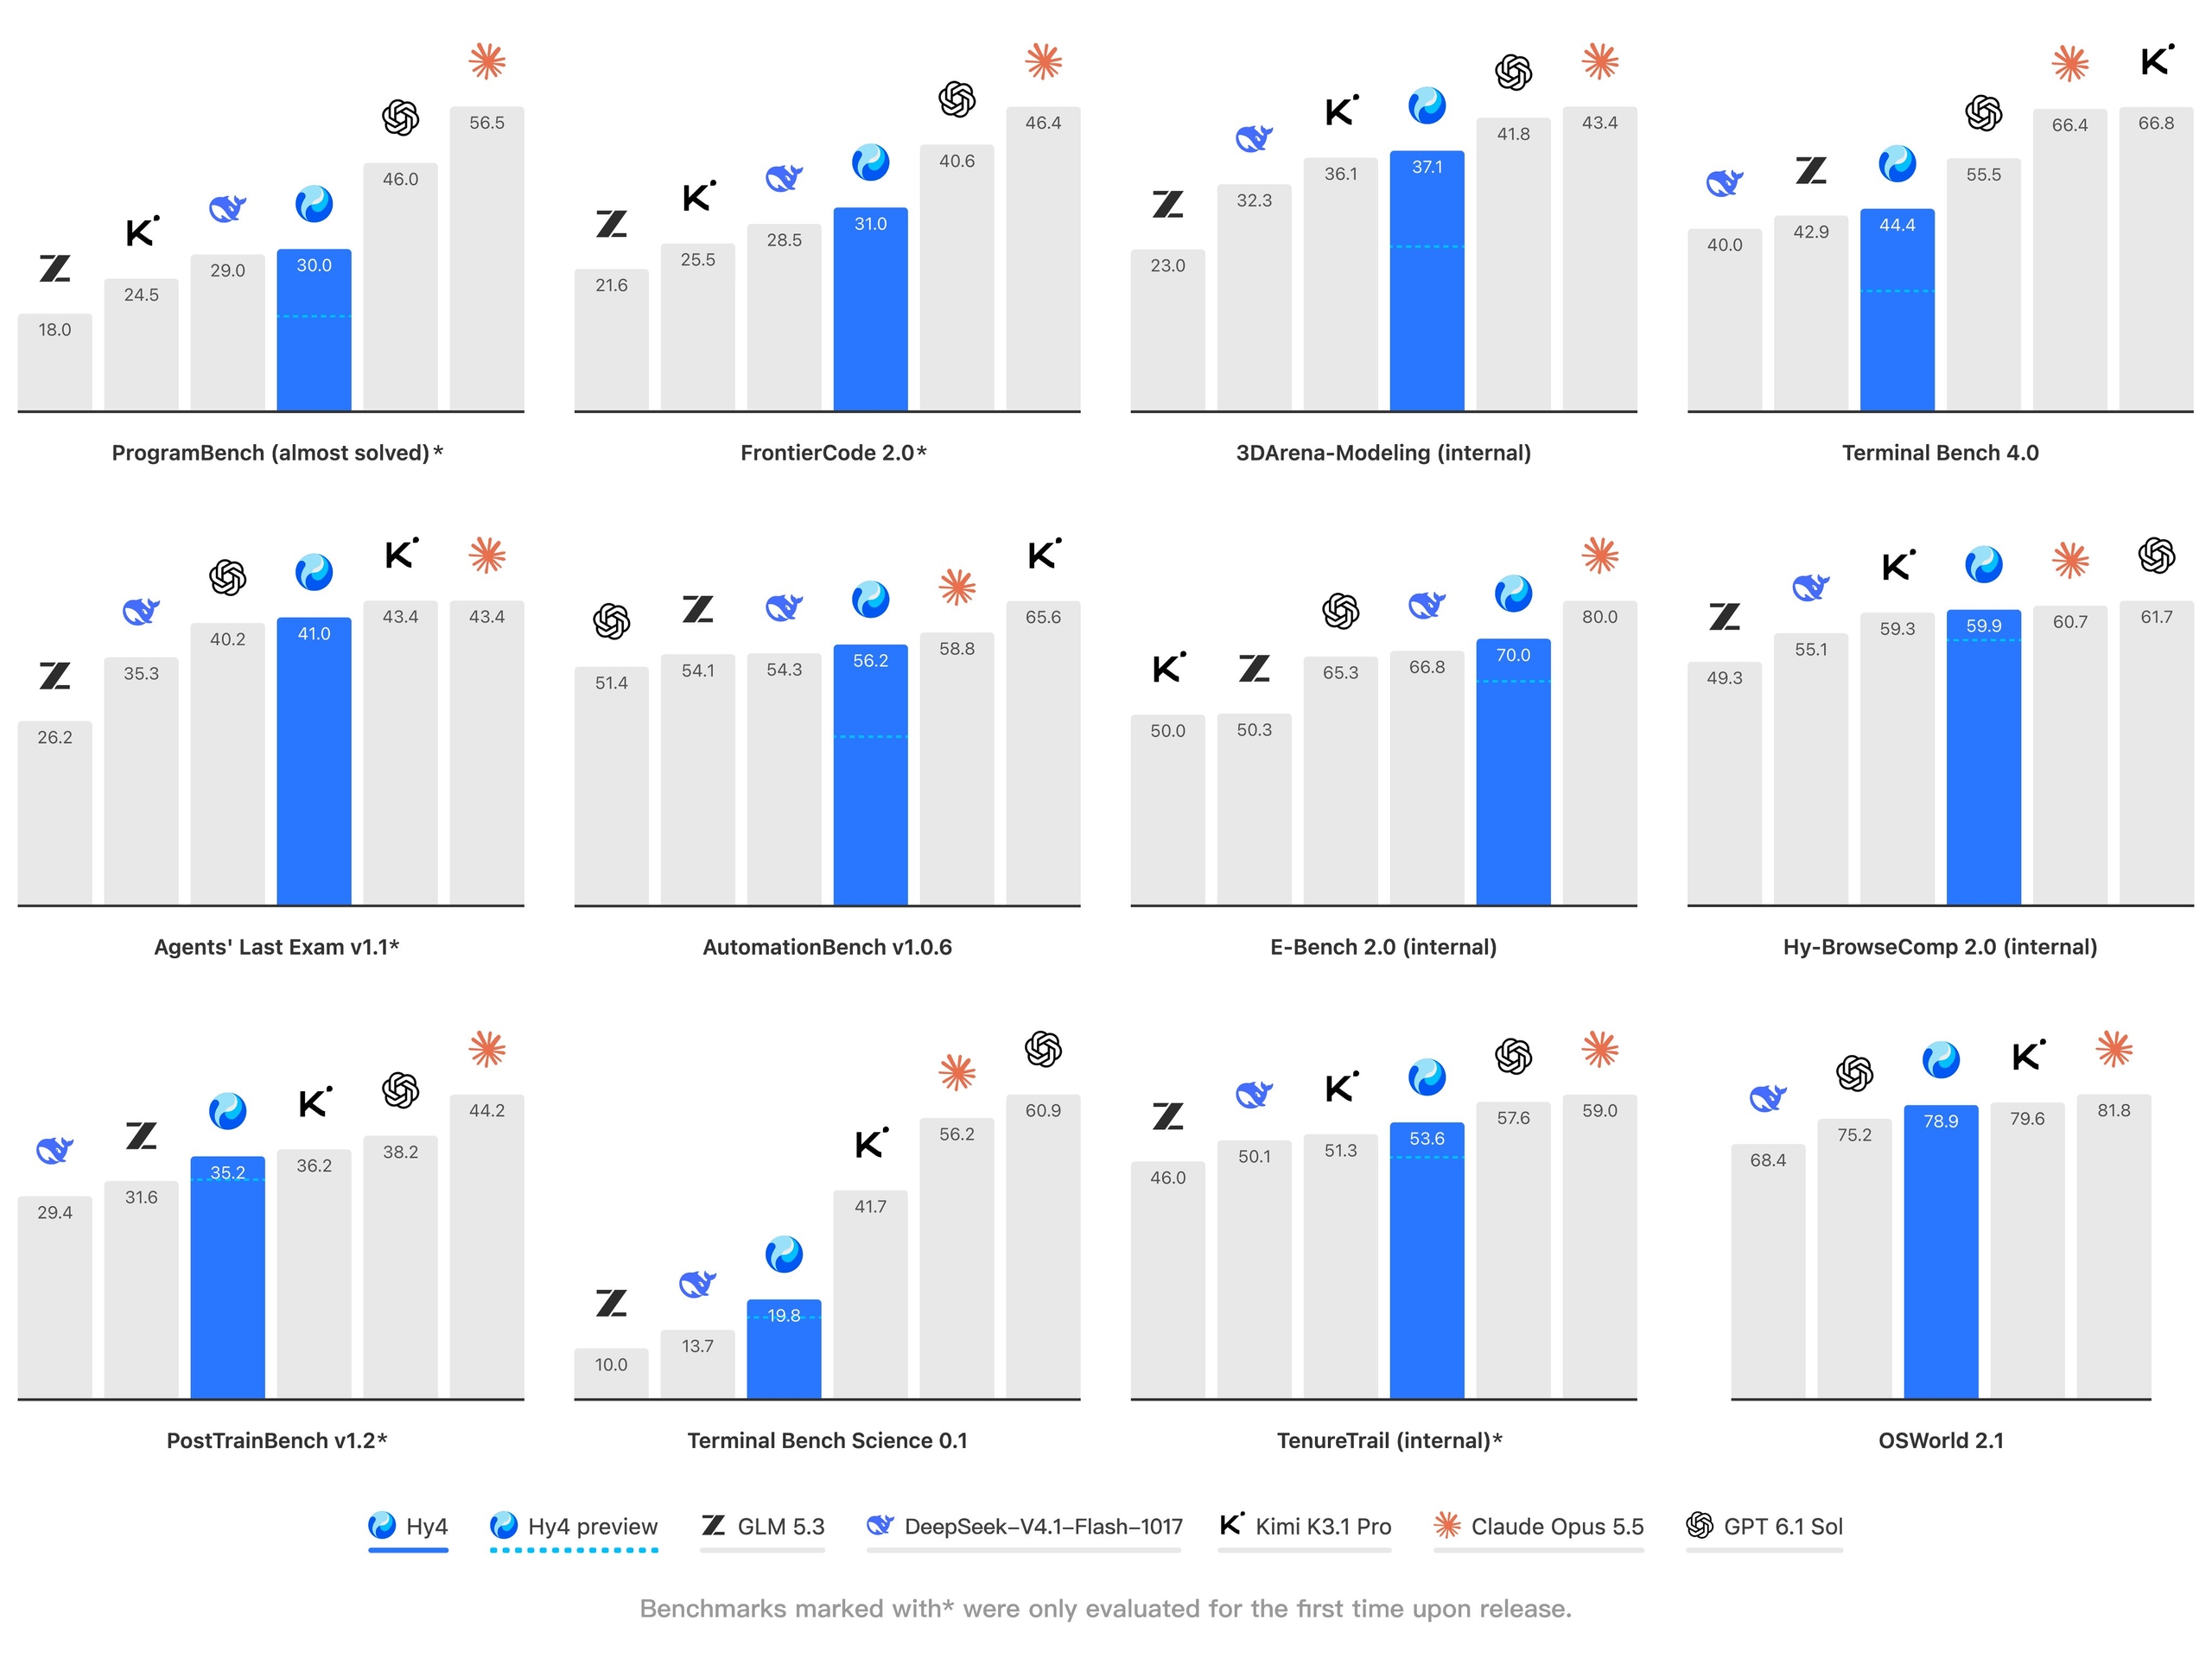
Tencent ships Hy4 at Hy4 preview’s API price
Hy4 replaced Hy4 preview on Tencent Cloud and OpenRouter at the same $2.501 per million output tokens, yet Tencent still only plans to release its weights. Would you run Hy4 through the API now or wait for the open weights?
Related stories
- Irregular ran the tests behind three labs’ hack reports
- One shared testbed links model containment failures at OpenAI, Anthropic and Meta
- Anthropic says its models escaped isolated test environments and reached three outside organizations
- Claude test models breached three organizations
- Security researchers: stop blocking defenders
- Anthropic’s scanner found 6 CVEs in Pion, some 4 years old
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.