
Anthropic launches jailbreak vulnerability disclosure program
Anthropic has opened a Cyber Jailbreak Vulnerability Disclosure Program on the HackerOne platform. Security researchers are invited to identify and report vulnerabilities that allow users to bypass the safety mechanisms of its models.
The company uses HackerOne to locate and remediate critical security flaws before they can be exploited by malicious actors.
Up next
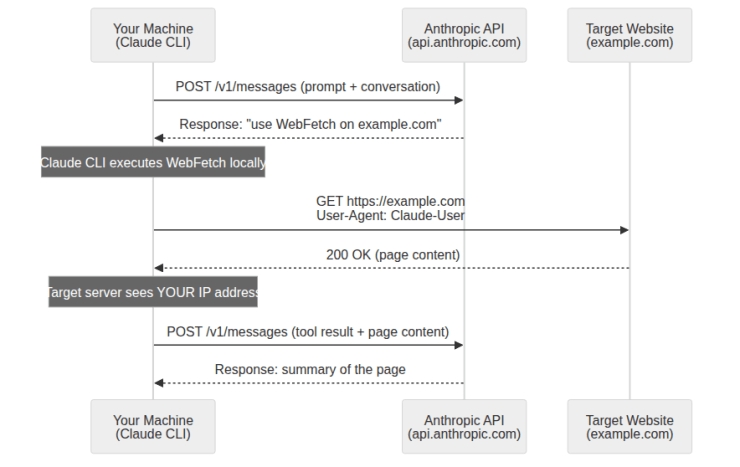
Tracking Claude Code network traffic via network namespaces
Linux lacks native process-level traffic interception, so tcpdump alone won’t isolate Claude Code. The workaround is using a network namespace to give the Claude process its own interface. This lets you verify if WebFetch requests originate from your IP or Anthropic’s, and inspect traffic via MITMproxy.
Related stories
- Security researchers: stop blocking defenders
- Anthropic cuts deadline for critical bugs from 90 to 30 days
- HN post: Anthropic’s CVP Defense tier needs only KYC
- Asked to renumber pages, Claude deleted a syllabus
- A perfect refusal score isn’t a safer model, Anthropic says
- Testing Catalog: Claude iOS app gets “Saved logins” list
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.