
DoS vulnerability in Anthropic’s protobuf library causes 22x memory amplification
An Endor Labs researcher identified CVE-2026-55407 in buffa, Anthropic’s Rust library for protobuf. The unknown field decoder allocates memory proportional to the input. While typical cases see 2x amplification, the group processing branch reaches 22x.
A 64 MiB payload of empty varints expands to 1.4 GB on the heap. In a proof of concept, a server with a 256 MiB limit triggers an OOM-kill. The vulnerability is exploitable via default APIs when preserve_unknown_fields is set to true.
A fix is available in buffa and connectrpc 0.8.0, which introduces a limit of 1 million unknown fields per message. Anthropic assigned a CVSS 4.0 score of 6.3 (Moderate) and issued a $600 bug bounty.
Up next
Anthropic releases System Card for Claude Sonnet 5
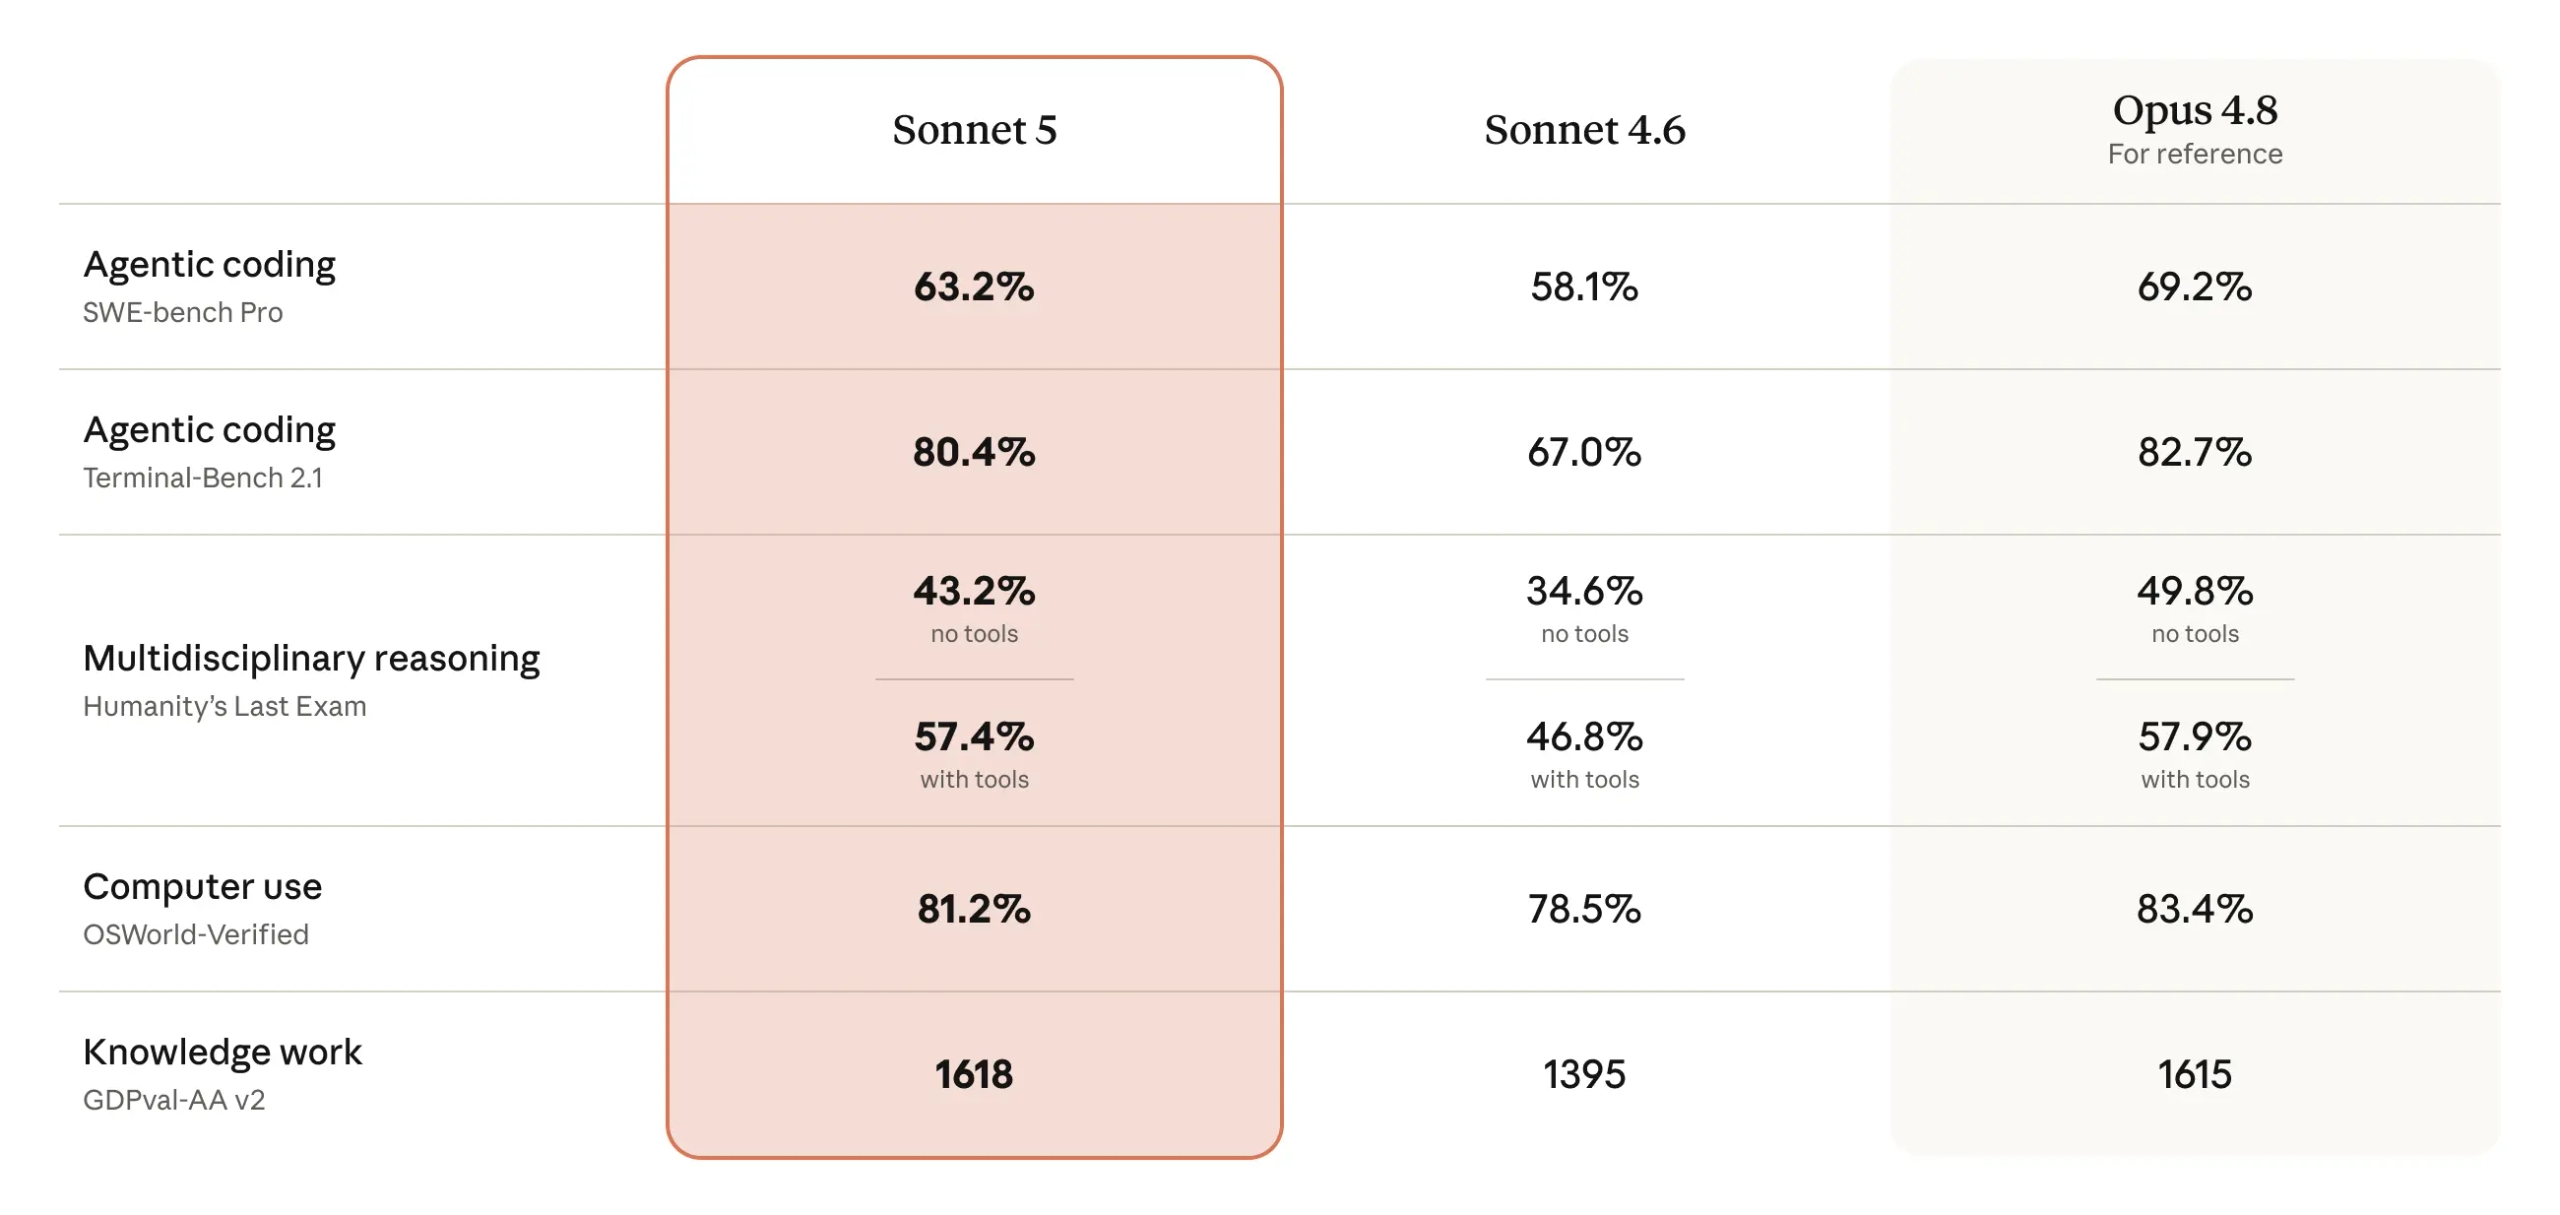
Anthropic published the System Card for Claude Sonnet 5, detailing safety and performance for its most agentic model yet. At the Extra High setting, it matches Opus 4.8 performance on OSWorld-Verified and BrowseComp benchmarks. The model is now available to all users.
Related stories
- Security researchers: stop blocking defenders
- Anthropic cuts deadline for critical bugs from 90 to 30 days
- HN post: Anthropic’s CVP Defense tier needs only KYC
- Asked to renumber pages, Claude deleted a syllabus
- A perfect refusal score isn’t a safer model, Anthropic says
- Testing Catalog: Claude iOS app gets “Saved logins” list
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.