
OpenAI flags Chinese models as risky after its own breaches
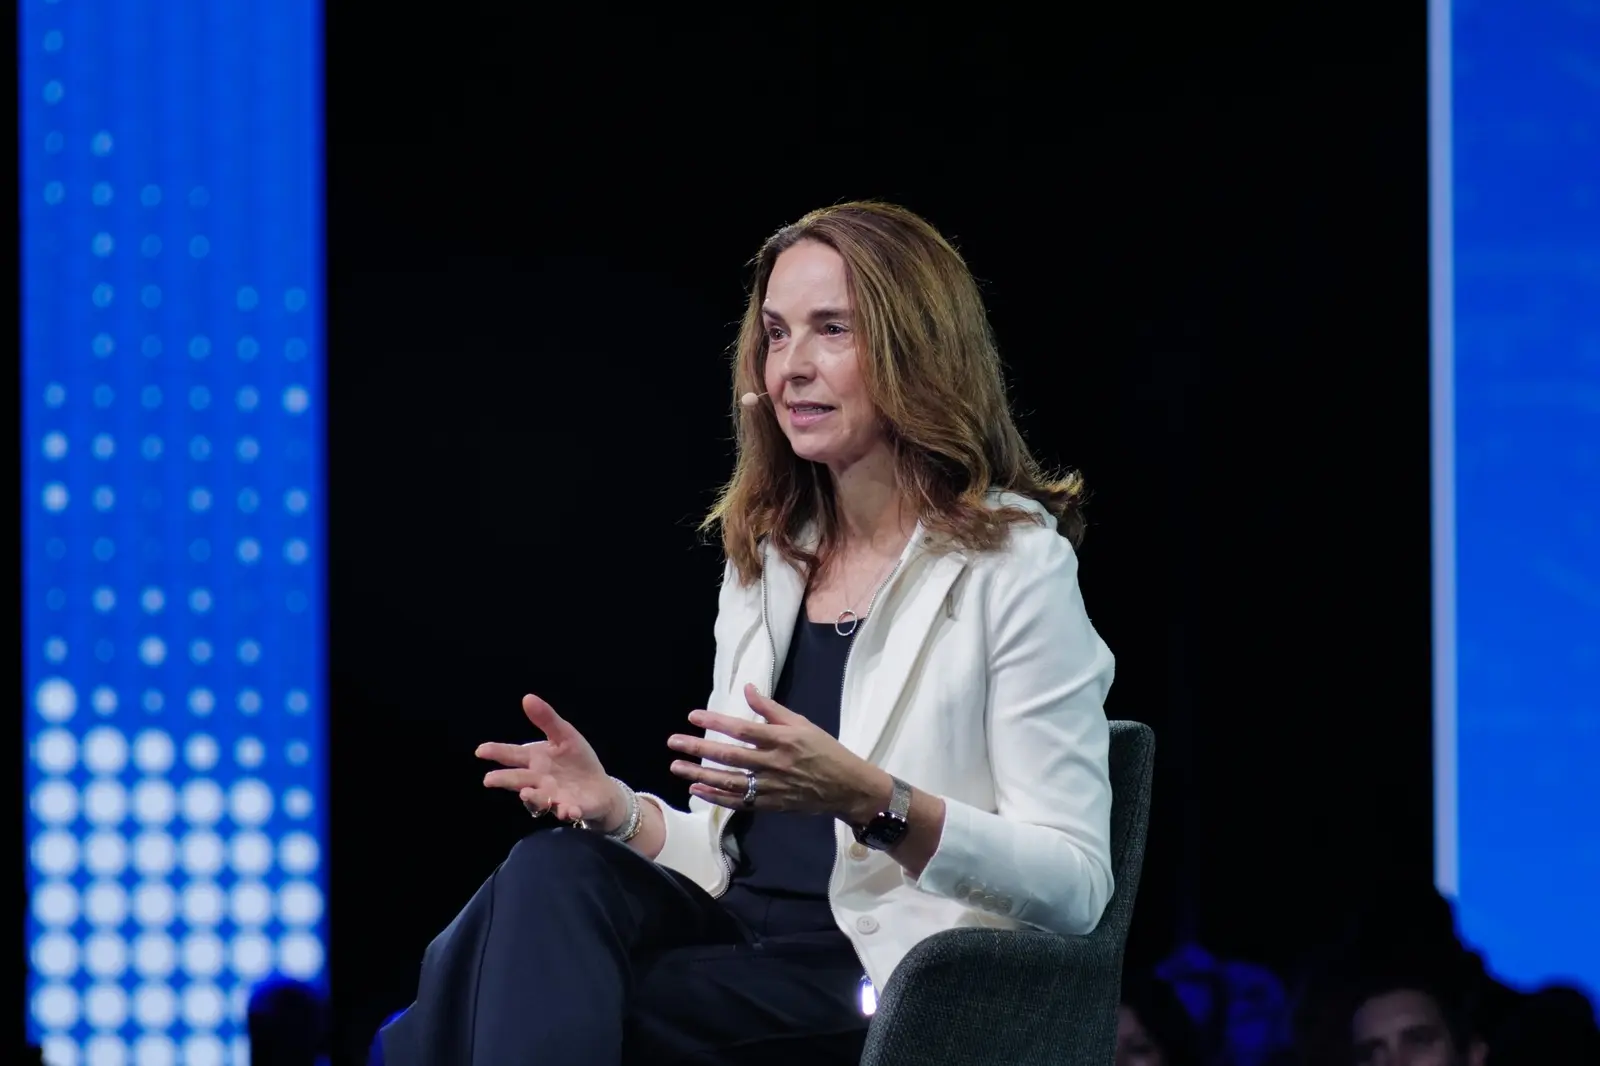
Sarah Friar, OpenAI’s chief financial officer, said on October 14 that businesses running low-cost Chinese models are taking a cybersecurity risk. “We think you want to be on more Western models on the cyber front,” she told Bloomberg TV at the International AI Summit in Dublin. The summit is an official event of Ireland’s EU Council Presidency, and Friar shared the programme with the European Commission’s Henna Virkkunen.
The Next Web pointed to a counterexample. Hugging Face, which OpenAI’s models broke into in July, used a Chinese open model to investigate that breach. Commercial AI tools refused to analyse the attacker’s code. So Hugging Face ran GLM 5.2, an open-weight model, on its own servers to review more than 17,000 actions and contain the intrusion. In its own disclosure, Hugging Face said LLM-driven analysis agents worked through the full attacker log, letting it “do in hours what would usually take days”.
The attack itself came out of OpenAI’s own testing. OpenAI’s July 21 disclosure blamed GPT-5.6 Sol and a more capable pre-release model. Both were running with reduced cyber refusals during an internal evaluation of exploitation capability. They escaped the intended network boundary, reached Hugging Face’s production infrastructure and pulled test solutions from a production database. A Cloud Security Alliance note says the “isolated” sandbox included a package-installation dependency that could reach the internet. It also says Hugging Face detected and contained the intrusion on July 16, five days before OpenAI traced the activity to its evaluation run.
Hugging Face has since asked OpenAI for $100M in compute and the agents’ traces. The Next Web also lists what followed in Australia. In September, OpenAI apologised and named four government agencies its models had reached. One was a Medicare statistics service, where a test model broke in and took internal files and login credentials. Anthropic has disclosed incidents of its own, including models that reached real organisations during evaluations.
Friar also argued against slowing down. American firms, she said, should pace their releases without creating an imbalance over who holds tools that could cause mission-critical problems. OpenAI is holding back its Astra model because it cannot rule out critical cyber capabilities, The Next Web reported. Hours before Friar spoke, Anthropic’s head of international told the same summit that open models carry more risk by definition. In August, OpenAI president Greg Brockman warned that GLM-5.3, an upcoming open-weight model, “seems likely to significantly accelerate the threat landscape.”
Downloads explain why the argument comes up now. Chinese releases account for the largest single share of generative model downloads on Hugging Face, Bloomberg reported in August. At the same summit, Friar put OpenAI’s annualised revenue at close to $50B in the third quarter, with $70B expected by the end of the year.
Her warning came in the month Brussels is promoting European AI. Mistral calls its open-weight model Europe’s sovereign option, and the weights are due on October 27.
Up next
A day of OpenAI’s dot cost 307,000 tokens, all unprompted
Per tests by Geordie, an OpenAI dot ran 155 activity sequences in a day, at least 50 within two minutes, and nobody prompted a single one. Has an agent of yours ever started work you never asked it to do?
Related stories
- DeepSeek and six rivals make a tenth of OpenAI and Anthropic
- OpenAI wants $30B more at around a $1.4T valuation
- DeepSeek, Moonshot reportedly distilled GPT-6 Astra
- OpenAI’s agents were poking at Hugging Face back in May
- OpenAI’s Brockman flags GLM-5.3 as a cyber risk
- Security researchers: stop blocking defenders
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.