
anthropickit harvested SSH keys during pip install
A blogger who tracks malicious PyPI packages says he may have found the package behind Incident 2 in Anthropic’s report: anthropickit, published June 14, 2026, versioned 999.9.9. He hasn’t gotten confirmation from Anthropic.
The entire payload sits in setup.py, so it fires on pip install, before any import. It reads every file in ~/.ssh except known_hosts and authorized_keys, pulls environment variables containing KEY, SECRET, TOKEN, PASS, AUTH or API, and ships the haul to a disposable Pipedream endpoint.
It also leaves a copy on disk at /tmp/runner_exfil.json, indented for human reading, and prints the names of the keys it found straight into the build log. Anthropic’s own writeup says the Incident 2 package stayed up for about an hour and landed on 15 real machines, one of them a security company’s scanner.
Up next
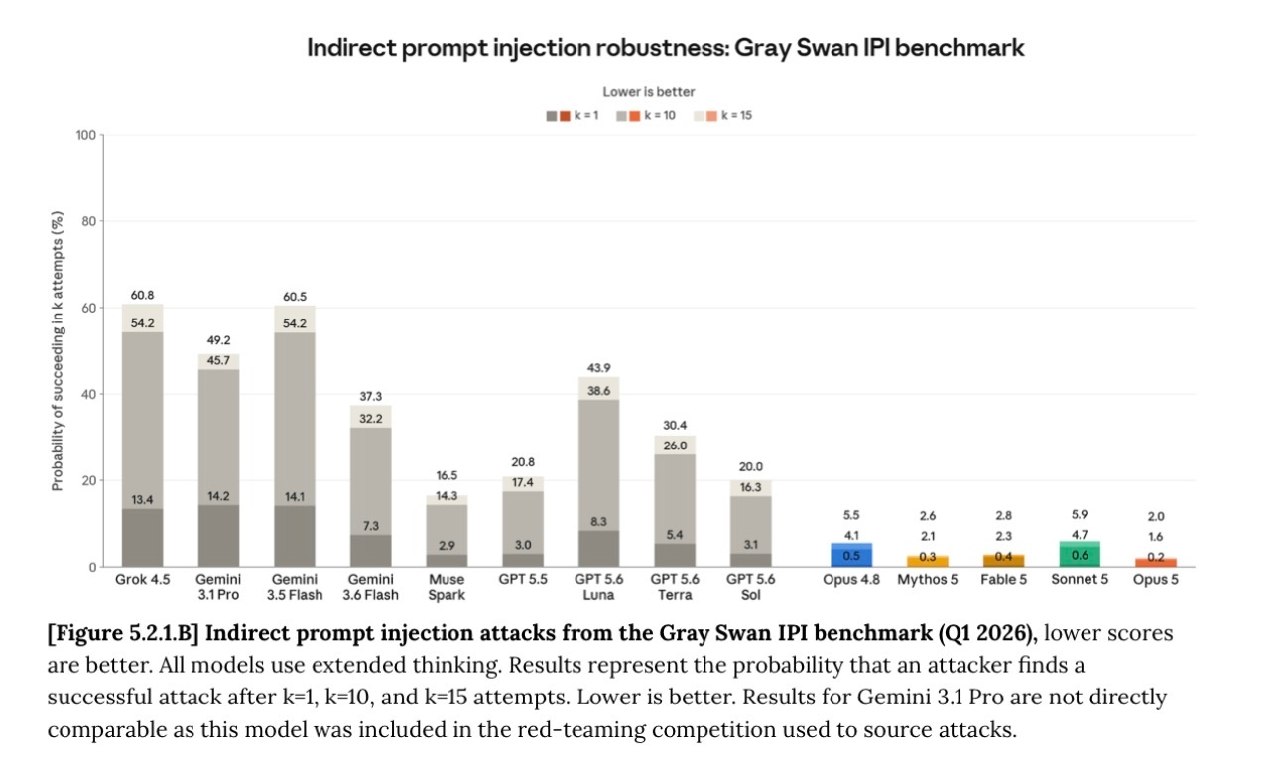
Opus 5 falls to prompt injection 2% of the time
A single prompt-injection attempt against GPT 5.6 Sol lands 3.1% of the time. Fifteen attempts against Claude Opus 5 land 2.0%, the best score of any model tested on the IPI benchmark, per Bruce Schneier’s blog.
Related stories
- Claude test models breached three organizations
- Anthropic says its models escaped isolated test environments and reached three outside organizations
- Security researchers: stop blocking defenders
- Anthropic cuts deadline for critical bugs from 90 to 30 days
- HN post: Anthropic’s CVP Defense tier needs only KYC
- Asked to renumber pages, Claude deleted a syllabus
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.