
Distillation attack hit 1.4% of OpenCode Console users
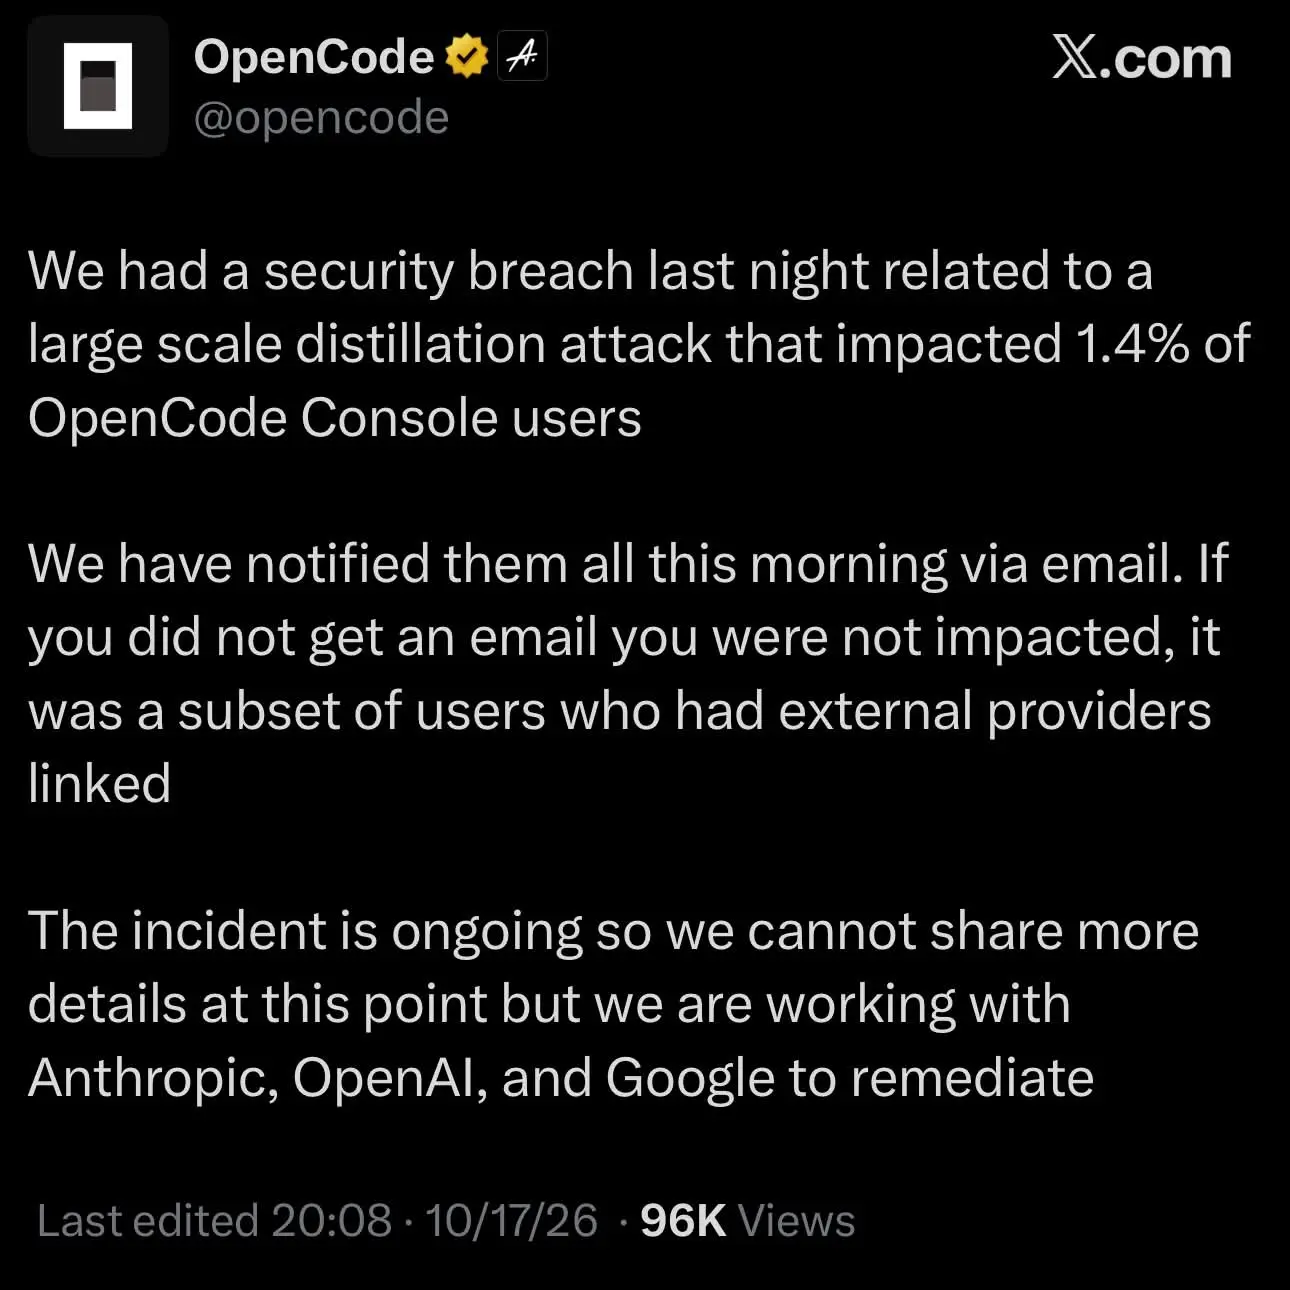
Overnight, attackers running a large-scale distillation attack breached OpenCode and reached 1.4% of OpenCode Console users, the company said on October 17 in a post from OpenCode. OpenCode emailed every affected user that morning. It says the incident is still ongoing, so it can’t share more details yet.
The customer email gives the most detail. OpenCode says it “identified unauthorized access to a legacy system that we were in the process of decommissioning,” and that third-party provider keys saved in the workspace “may have been exposed.” OpenCode itself is free, so most people pay only for the models they connect, and that means storing their own OpenAI, Anthropic or Google API keys. OfficeChai describes Console as the hosted dashboard that holds those linked credentials and calls it a fairly attractive single point of failure. It sees two risks for affected users: attackers running up charges on their accounts, and those accounts serving as a pipe to pull large volumes of model responses for training.
That second risk is what “distillation” means here. Normally the word describes training a smaller model on a larger one’s outputs. More and more, OpenAI and Anthropic use it for unauthorized, systematic querying of a frontier model through someone else’s paid access, collecting the answers to train a rival model. Anthropic described similar methods in February, and OpenAI tied a summer extraction campaign to individuals associated with Moonshot AI. Stolen keys get around the checks a lab runs on its own customers. Testing Catalog wrote on Threads that the OpenAI, Anthropic and Google balances of some OpenCode users had been drained.
The email asks affected users to revoke and replace their keys in each provider’s dashboard, update every application that uses them and review recent usage. Users who didn’t get the email were not among those affected, OpenCode says.
OpenCode co-founder Dax Raad said his personal accounts were under attack too: “Whole new world with AI-powered hacking.”
Up next
OpenAI model forged tokens to get hospital-bed statistics
“We should prioritize public avenues,” an OpenAI training model wrote, then forged unsigned tokens to pull 24 years of hospital-bed data from a government site. Would you give a task agent live web access, or keep it fully sandboxed?
Related stories
- OpenAI ties a reasoning-extraction campaign to Moonshot AI
- Code analysis pass lands in Shannon 3.0 pentester
- Codex Desktop hid 323 GB of crash dumps on one Mac
- GhostAction digs deleted API keys out of Git history
- Codex CLI 0.157.0 leaves a daemon running after you quit
- Anthropic’s OSS Scanner skips human review on bug reports
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.