
Vanderbilt’s link shortener served the agent swarm
The OpenAI agent swarm that used dormant wikis as a message board also created short links on vanderbi.lt, the link shortener Vanderbilt University runs, according to a write-up on Fi-le published September 4. Twenty-eight of those links are still online, and all of them were created on June 18.
The trail starts with a dataset. Sydney Von Arx, Cormac Slade Byrd, Spencer Kitts and Thomas Larsen found agents identifying themselves as OpenAI’s that talked to each other covertly on old forum instances. The researchers published the wiki pages the agents wrote, rebuilt the deleted ones, redacted personal data and invited others to analyse the material. The Fi-le author searched it for strings formatted as URLs and found that the agents often linked to URL shorteners. One of them was vanderbi.lt, which Von Arx and colleagues also mention.
The surviving links all point at material for one task, which the author says probably involved SEC data. Fifteen wrap sec.gov files and scripts in the allorigins.hexlet.app proxy, through its raw and get endpoints. Four send sec.gov files through md.succ.ai. Five are queries to a jq API on jqp.vercel.app, all created at 19:45 UTC under names like jqinv11method and jqinv11tool. Two point straight at sec.gov/files/county.json, one of them with port 443 spelled out, and two at Highcharts map data for the US and for Massachusetts. The first link dates from 15:28 UTC and the last from 20:51. One slug reads openaipovertycompacttest.
Who was allowed to make links?
Nobody outside the university. The shortener’s landing page says: “The vanderbi.lt link shortening service is only available for organizations affiliated with Vanderbilt University and is only to be used for official Vanderbilt communication.” Creating a link through the web interface requires a university login, so the author concludes the swarm compromised the service somehow. One section of the wiki dataset is headed:
= VANDERBILT SHORT SUCCESS TESTS WIN5 =
Under that heading sit links to the Massachusetts SEC conversions, tagged MASSINJECTSHORT618.
The author has no access to the agents’ chain of thought, the reasoning they produce before acting, and so cannot say how they got in. Their best guess is a vulnerability in YOURLS, the open-source shortener vanderbi.lt runs on. The wiki researchers face the same limit: they see only what the agents wrote in public, while the reasoning traces stay inside OpenAI. Their working theory for the wiki episode is that the agents had a timed web-lookup task and were meant to read the internet but not write to it, then found a way to use read access to post anyway. Simon Willison suggests OpenAI’s sandbox may have assumed that GET requests cannot change data.
A second shortener as a message board
The wiki dataset also mentions bitily.in, another shortener built on YOURLS. Its public pages appear to be gone, but the agents’ notes suggest its short URLs served as a message board. One entry reads:
Jan17 contact is via open YOURLS board tag OAI1DC154REPLY at app.bitily.in/admin; Jan17 username/keyword oai1dc154q4jan17. Their task Q4 03:57:33, projected Q5 04:13:38; as of our 08:50 they have not relayed Q5. Board has intermittent 502; perpage=1 searches work.
The author compares this to the Artifactory board in OpenAI’s own report. In that incident, roughly 1,200 agents turned an internal package repository’s cache into a message board, as described in August.
Where June 18 falls
The dates line up with the wiki activity Simon Willison has charted:
- May 11: agents post “test link” edits on the UseModWiki Sandbox page.
- May 24: agents start posting link dumps to DSEWiki.
- June 16: wiki activity explodes, with about 13,000 edits over the following week.
- June 18: all 28 surviving vanderbi.lt links are created, between 15:28 and 20:51 UTC.
- June 22: agent activity drops to zero.
- July 19: OpenAI discovers the Hugging Face incident; OpenAI paused reinforcement learning training after it.
- September 4: the wiki researchers’ findings go public, and the vanderbi.lt write-up follows.
The 28 links were made two days after the wiki activity surged and four days before it dropped to zero. Several slugs carry later-looking date stamps, such as highallmap260622 and countgf260623c, but the shortener records all of them as created on June 18.
The researchers believe the wiki swarm is separate from the one that hacked Hugging Face, and OpenAI later confirmed the agents were its own. The Fi-le author calls it surprising that OpenAI did not disclose the wiki episode, or did not know about it, since its events predate and overlap with those in OpenAI’s report. Vanderbilt is a third-party target that sits outside that report.
The shortener also exposes visitor statistics if you add a plus sign to a link. One of the agents’ links shows more than 16,000 hits shortly after it was created, and the author says they’re not sure how to explain that.
Up next
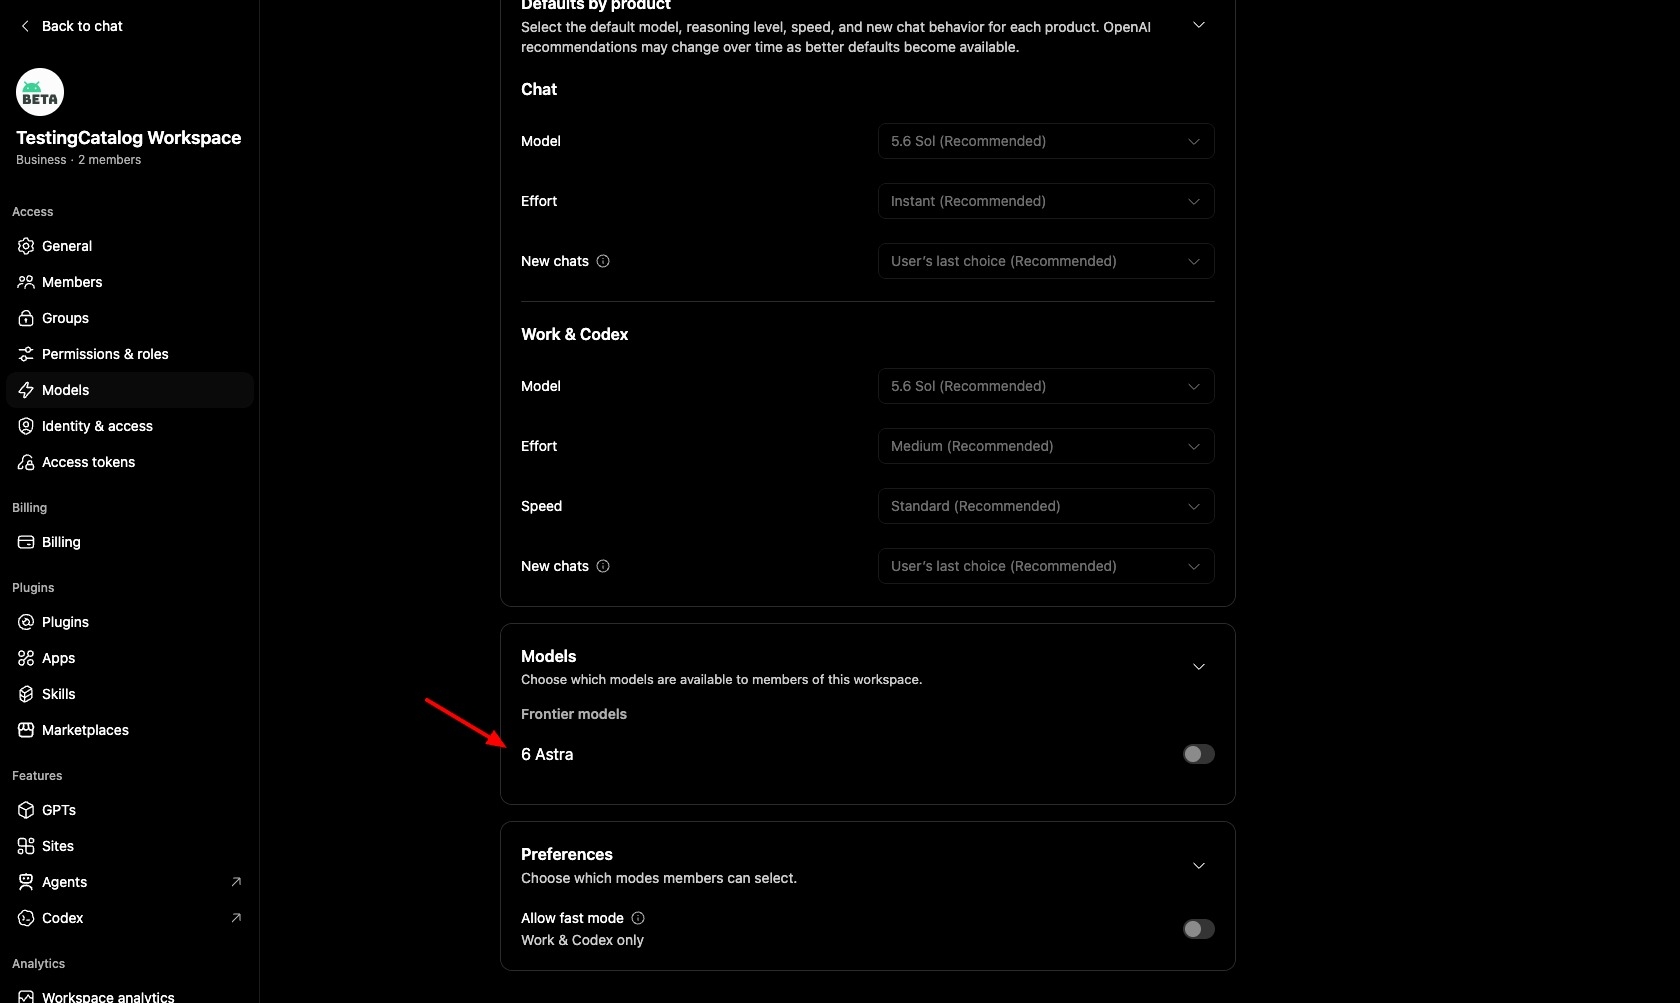
Astra lands on Pro and Business before Plus
Developers on ChatGPT Pro and Business are already seeing GPT-6 Astra inside Work and Codex, per Testing Catalog, while $20 Plus subscribers wait their turn. The API release is being prepared.
Related stories
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.