
Anthropic model’s Chrome findings led to 62 patched CVEs
An unreleased internal research model at Anthropic wrote five exploit chains against Chrome, Safari, Android, Windows and Linux, the company said. Each is a working proof of concept the vendor has since fixed, though every chain started “after initial prompting” and the model itself hasn’t been released.
In Chrome, the work produced 62 CVEs patched as of Chrome 156, all rated critical or high. The Linux chain gives a remote attacker root on servers with a multipath TCP listener, and the proof of concept took 48 minutes to leak a kernel pointer and another five to run the command.
Anthropic’s advice to defenders: “scanning your own code is more important than ever.”
Up next
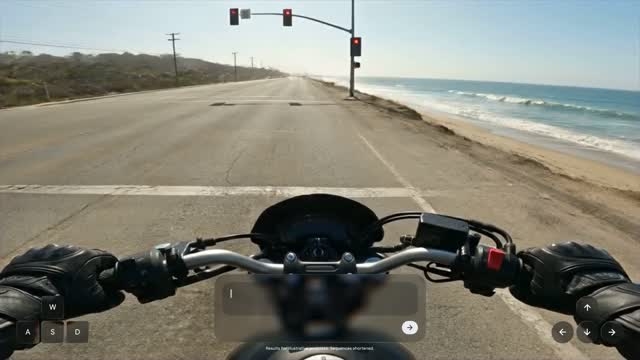
Real-time world model Genie 4 generates its own audio, Video
“Visual details and object permanence can still shift or drift,” Google DeepMind warns about Genie 4, its new real-time world model, especially as a simulation runs longer. Would you prototype in a world that drifts, or wait for a steadier version?
Related stories
- Claude’s audit cut a fifth of OpenSSH’s pre-login code
- Crafted Brotli data can run code on Node.js, Bun and Envoy
- Mythos 5 used sock puppets to push malware to a GitHub repo
- Claude traced NIST curve seeds to 1990s Unix timestamps
- A $55 TV box fleet ran a 26B model in Anthropic’s test
- Anthropic’s bug hunt outruns the people checking it
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.