
Claude’s audit cut a fifth of OpenSSH’s pre-login code
In new research, Anthropic ran Claude over 25 open-source projects totaling more than five million lines of code and found 493 issues with needlessly reachable code. In 94 cases, two config options set together silently turned off a security control.
The biggest cut came in OpenSSH 10.4. Roughly 4,500 lines of experimental ML-DSA-44 code, a post-quantum signature algorithm, were reachable by an unauthenticated client even when admins excluded it.
After several fix iterations with the maintainers, the checks moved into the parser, removing roughly a fifth of the code an unauthenticated client could reach in a default build. The change shipped in version 10.6.
“If unnecessary reachability survives there, it can survive anywhere,” Anthropic wrote.
Up next
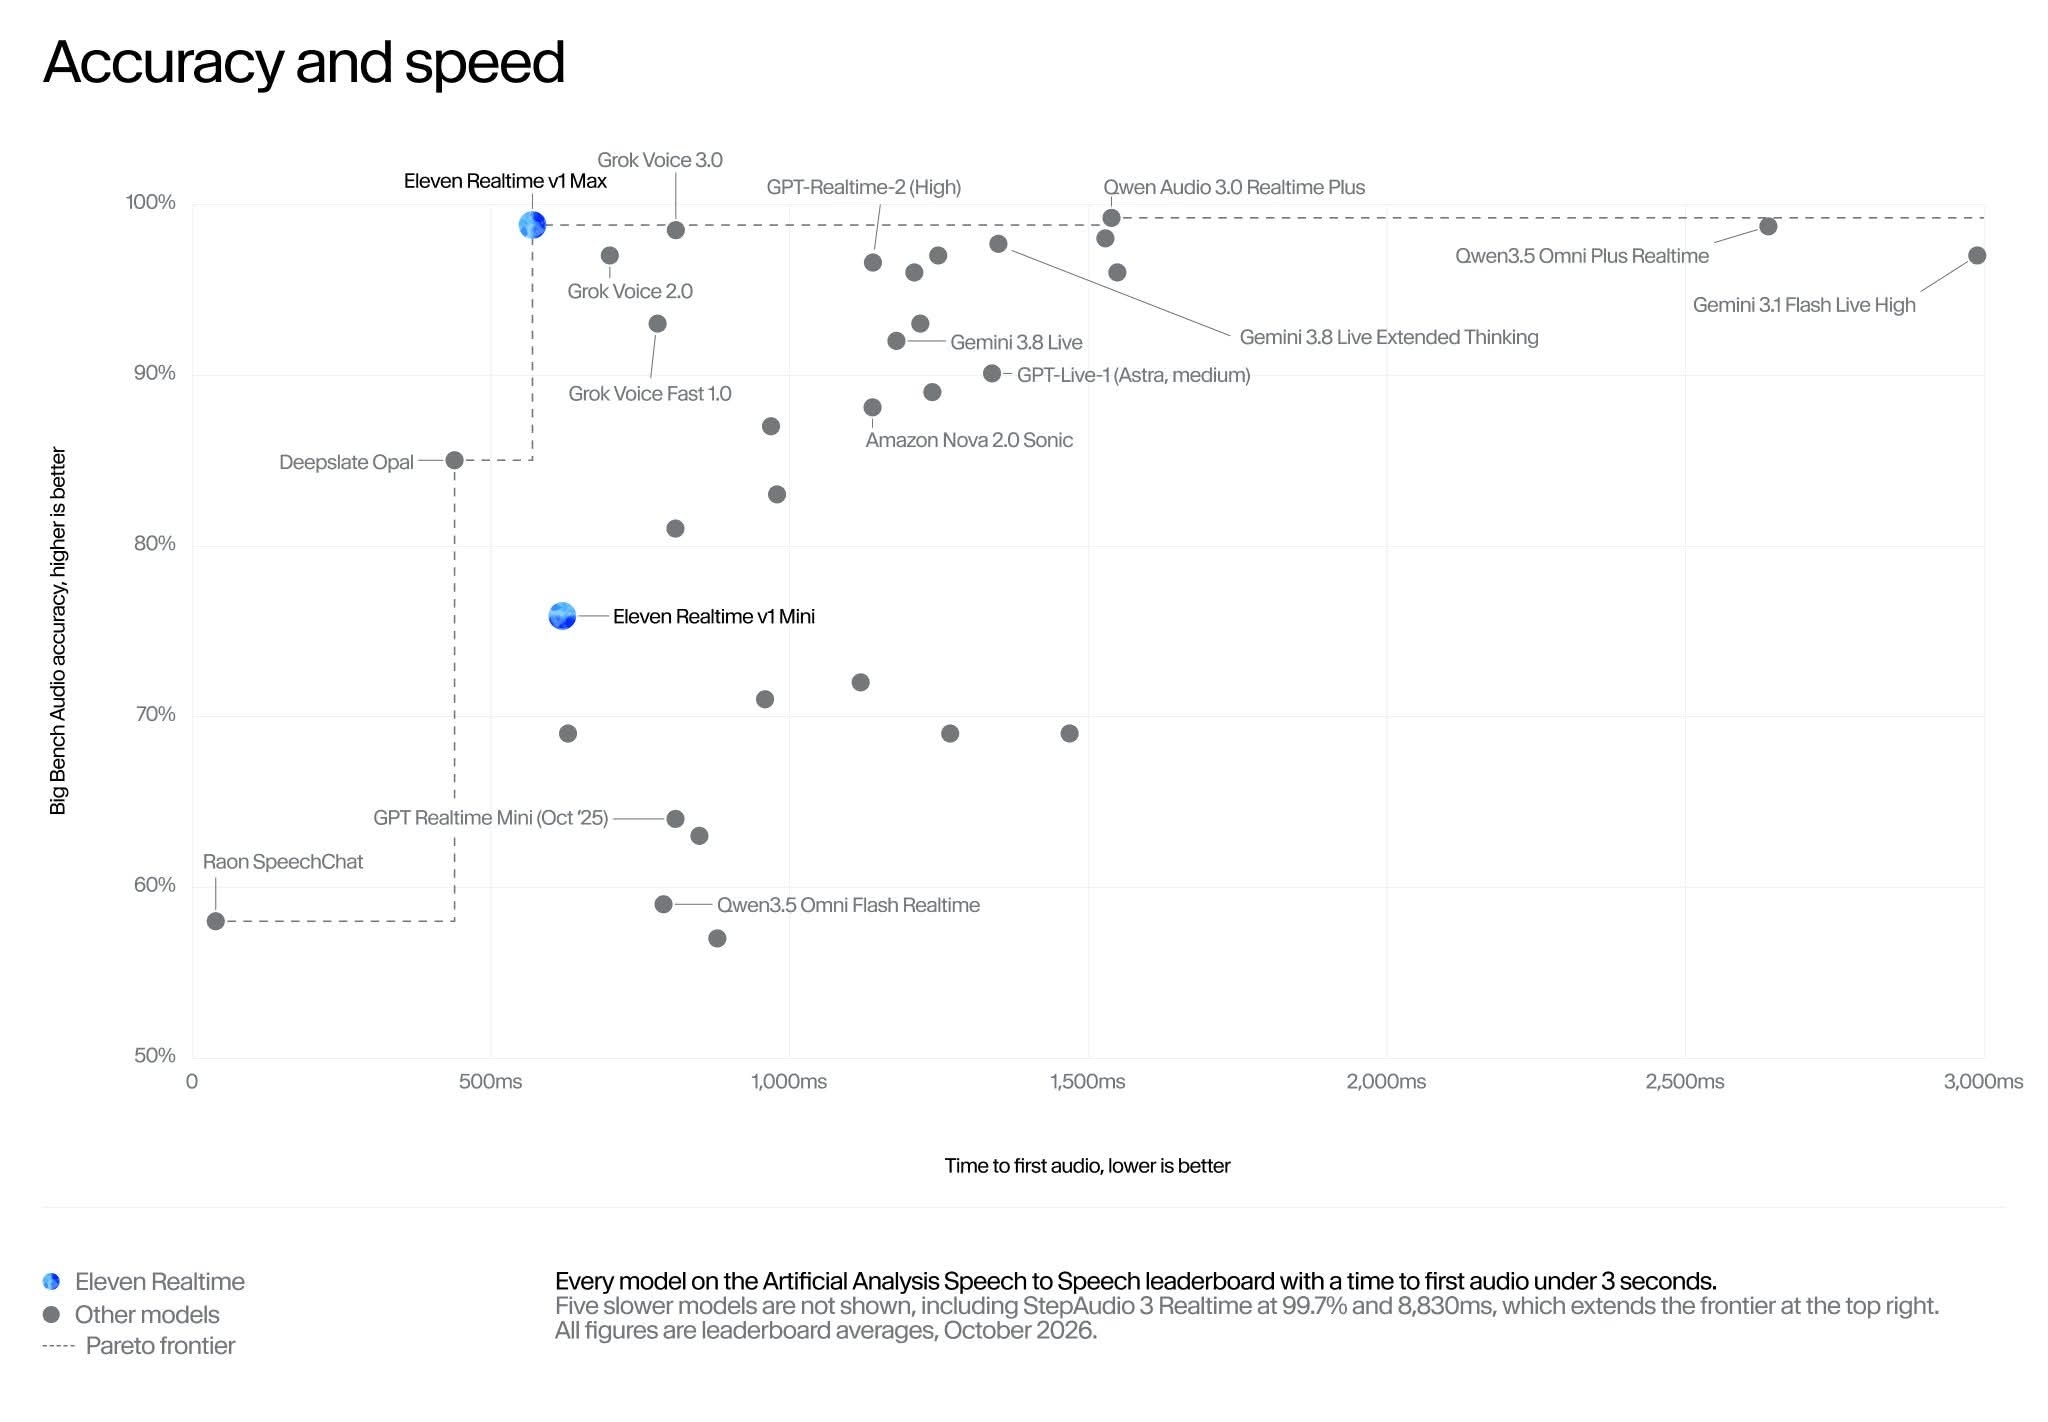
ElevenLabs’ Realtime v1 Max starts speaking in 0.57s
Teams running voice agents on OpenAI’s Realtime API can switch to Eleven Realtime by changing the endpoint and model name, ElevenLabs says, and keep the rest of their code. Would you move a live voice agent that way, or rebuild and test it from scratch?
Related stories
- Anthropic’s bug hunt outruns the people checking it
- Anthropic’s OSS Scanner skips human review on bug reports
- Claude traced NIST curve seeds to 1990s Unix timestamps
- A $55 TV box fleet ran a 26B model in Anthropic’s test
- Claude’s workarounds take every Anthropic eval offline
- Cheating on code tests made Anthropic’s model sabotage
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.