
Claude Code approvals put keys in 1,122 public GitHub files
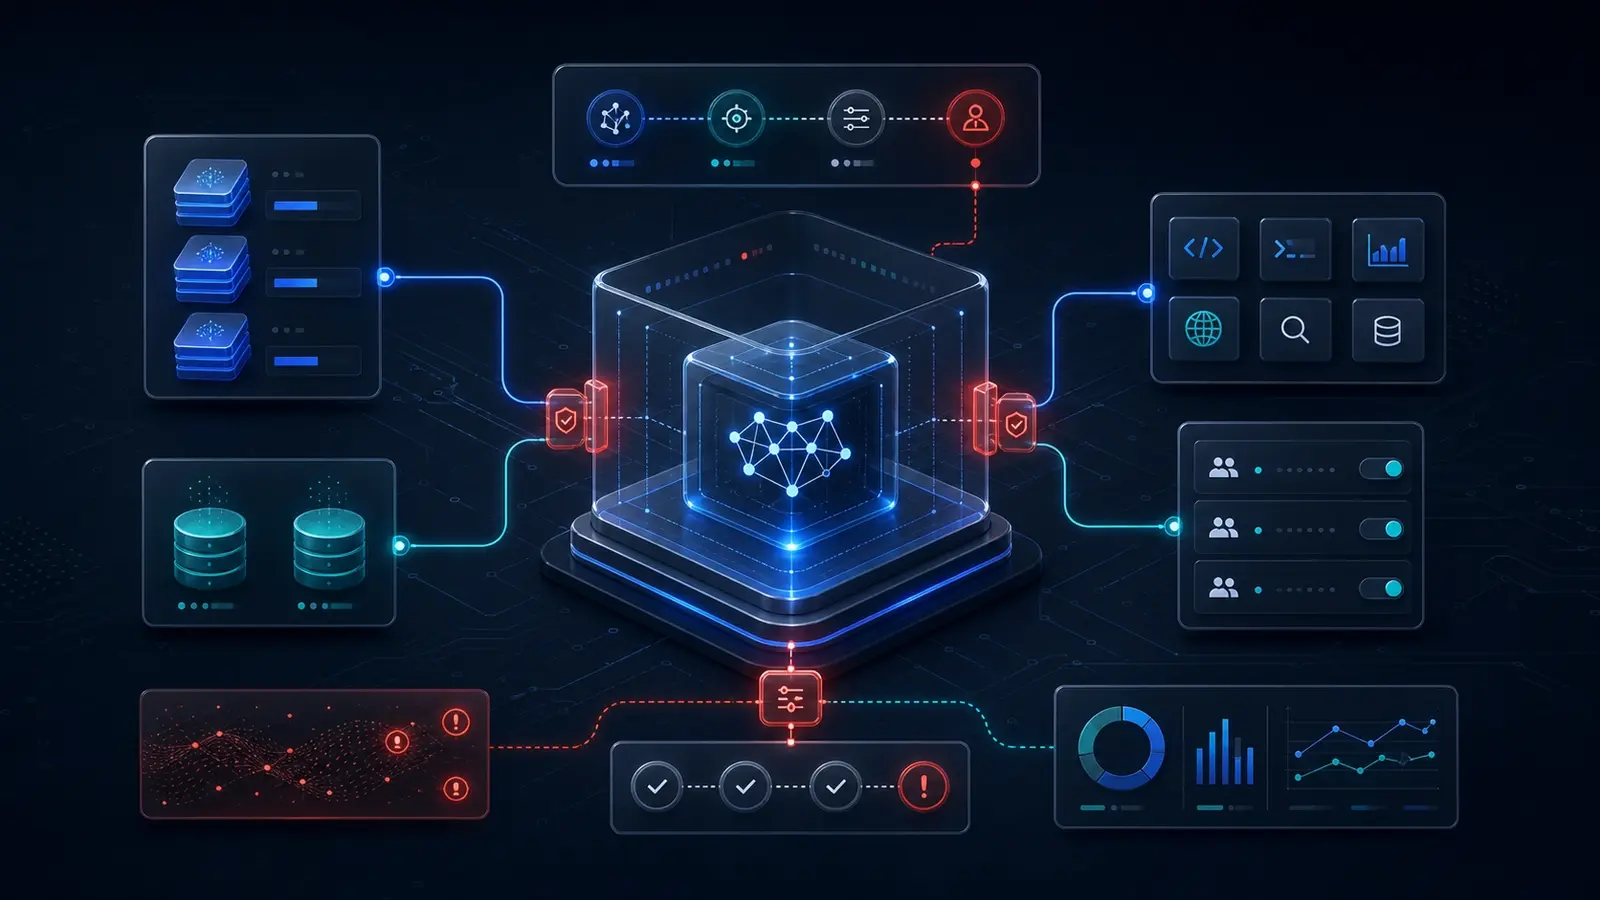
If you’ve approved a Claude Code command containing a password or API key with “Yes, and don’t ask again,” that secret may be stored word-for-word in a project settings file, security firm Apiiro found. Those files end up committed to public GitHub repositories, and the exposure is reported as affecting 1,122 public files.
The file is .claude/settings.local.json, and in many cases Claude was listed as co-author of the commit that published it, according to Aviatrix.
Up next
OpenAI’s dots can now read email codes to pass 2FA, Video
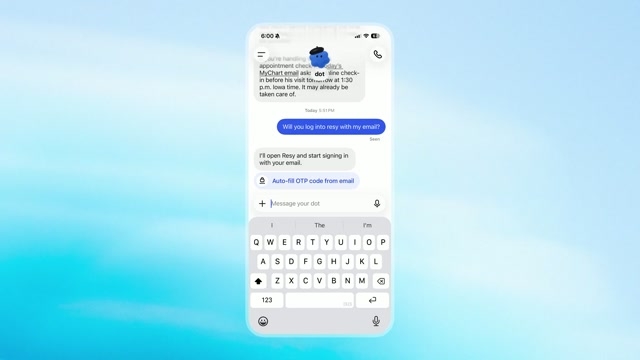
OpenAI’s dots gained a new skill, reading sign-up codes from your email to finish a 2FA check for you, though reports differ on whether they enter the code or pause first. Would you let an agent read the inbox where your 2FA codes arrive?
Related stories
- Claude Code hashes files for Anthropic even on DeepSeek
- Fake coverage report stole keys via Claude Code Desktop
- Claude Code put users’ emails in User-Agent headers
- Tainted Claude Code build stayed in Cursor, Microsoft finds
- Claude Code env var lifts its last block on rm -rf ~
- Anthropic open-sources Claude Code’s sandbox runtime
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.