
Six curl CVEs land after two AI scanners found none
Curl founder Daniel Stenberg posted a score of “Mythos: 0 Aisle: 29” one day after writing that frontier AI scanners had nothing left to find in his code. Six of those 29 reports from AISLE, an AI security startup, are now CVEs fixed in curl 8.22.0, the company said in a September 2 post on the AISLE blog. All six credit AISLE’s Stanislav Fort as the reporter.
The comparison runs against a public baseline. In an August 24 post, Stenberg wrote that only three CVEs were pending for the next curl release. He had run frontier AI security systems over the code, and he reported what they found: ”[Anthropic] Mythos says it can’t find any more. ... [OpenAI] Codex security shows an empty list.” AISLE says it pointed its autonomous system at curl after Stenberg had documented the Mythos results. Curl is deployed across more than 20 billion instances worldwide, from smart fridges to spacecraft, and AISLE calls it one of the most heavily audited codebases in the world.
Fort filed three of the eventual CVEs on August 24, the same day Stenberg wrote that Mythos could not find any more. Two more followed on August 26 and the last on August 27. Stenberg’s 0-to-29 post went up on August 25, already, before curl’s security team had finished reviewing the reports, so the 29 counts reports. Six of them made it through review to a CVE designation:
- CVE-2026-80229: OpenSSL provider use-after-free
- CVE-2026-80230: OpenSSL pinning bypass
- CVE-2026-80231: native CA store connection reuse
- CVE-2026-80255: secure attribute bypass with tab
- CVE-2026-82208: wolfSSL CA-cache hit overrides callback
- CVE-2026-82209: domain-scoped public-suffix cookie
Every one of the six is rated Low severity. AISLE puts that down to curl’s “exceptional engineering maturity”, saying the bugs that remain “tend to hide in narrow configurations and subtle interactions, limiting their practical impact.”
What a report costs curl
Reviewing 29 reports is real work for curl. In a July 2025 post, Stenberg wrote that the security team has seven members and that each report pulls in three or four of them, perhaps for 30 minutes each, sometimes up to an hour or three. In the same post he put AI slop at about 20% of all submissions to curl in 2025, at an average of about two security reports a week.
Curl ended its bug bounty at the end of January 2026. Stenberg said the shutdown would “remove the incentive for people to submit crap and non-well researched reports to us. AI generated or not.” AI-assisted reports had held up before, though. In September 2025 security researcher Joshua Rogers sent in a long list of potential issues found with AI-assisted tools, and it produced 50 real bugs. Stenberg called them “actually, truly awesome findings.”
Why AISLE says the result counts
AISLE argues that the setup is what gives the result weight. It was not a capture-the-flag exercise or a benchmark whose answers might already sit in a model’s training data. The code was current production curl, and curl’s maintainers decided whether each finding was real and whether it deserved a CVE. Because Stenberg published the zero result before AISLE ran its system, the company says the baseline was “public and timestamped before our result existed.” It also concedes that “CVEs are imperfect markers”, but calls them strong outside validation, since each one is a previously unknown flaw that domain experts reproduced, accepted and fixed for users.
The company presents curl as support for what it calls its “System over Model” thesis: a specialized AI system can compete with and outperform the frontier labs’ own systems at finding zero-days in real code. It sells the same engine as a one-time audit called AISLE Snapshot. AISLE also says the pattern may reach beyond curl, pointing to Greg Kroah-Hartman, the longtime maintainer of Linux stable releases, who replied to Stenberg’s post: “I’m seeing the same for Linux as well. No idea what Aisle is doing differently, but wow...”
By August 28, curl’s pending CVE count had gone from the three Stenberg mentioned on August 24 to ten. Six of those ten came from AISLE.
Up next
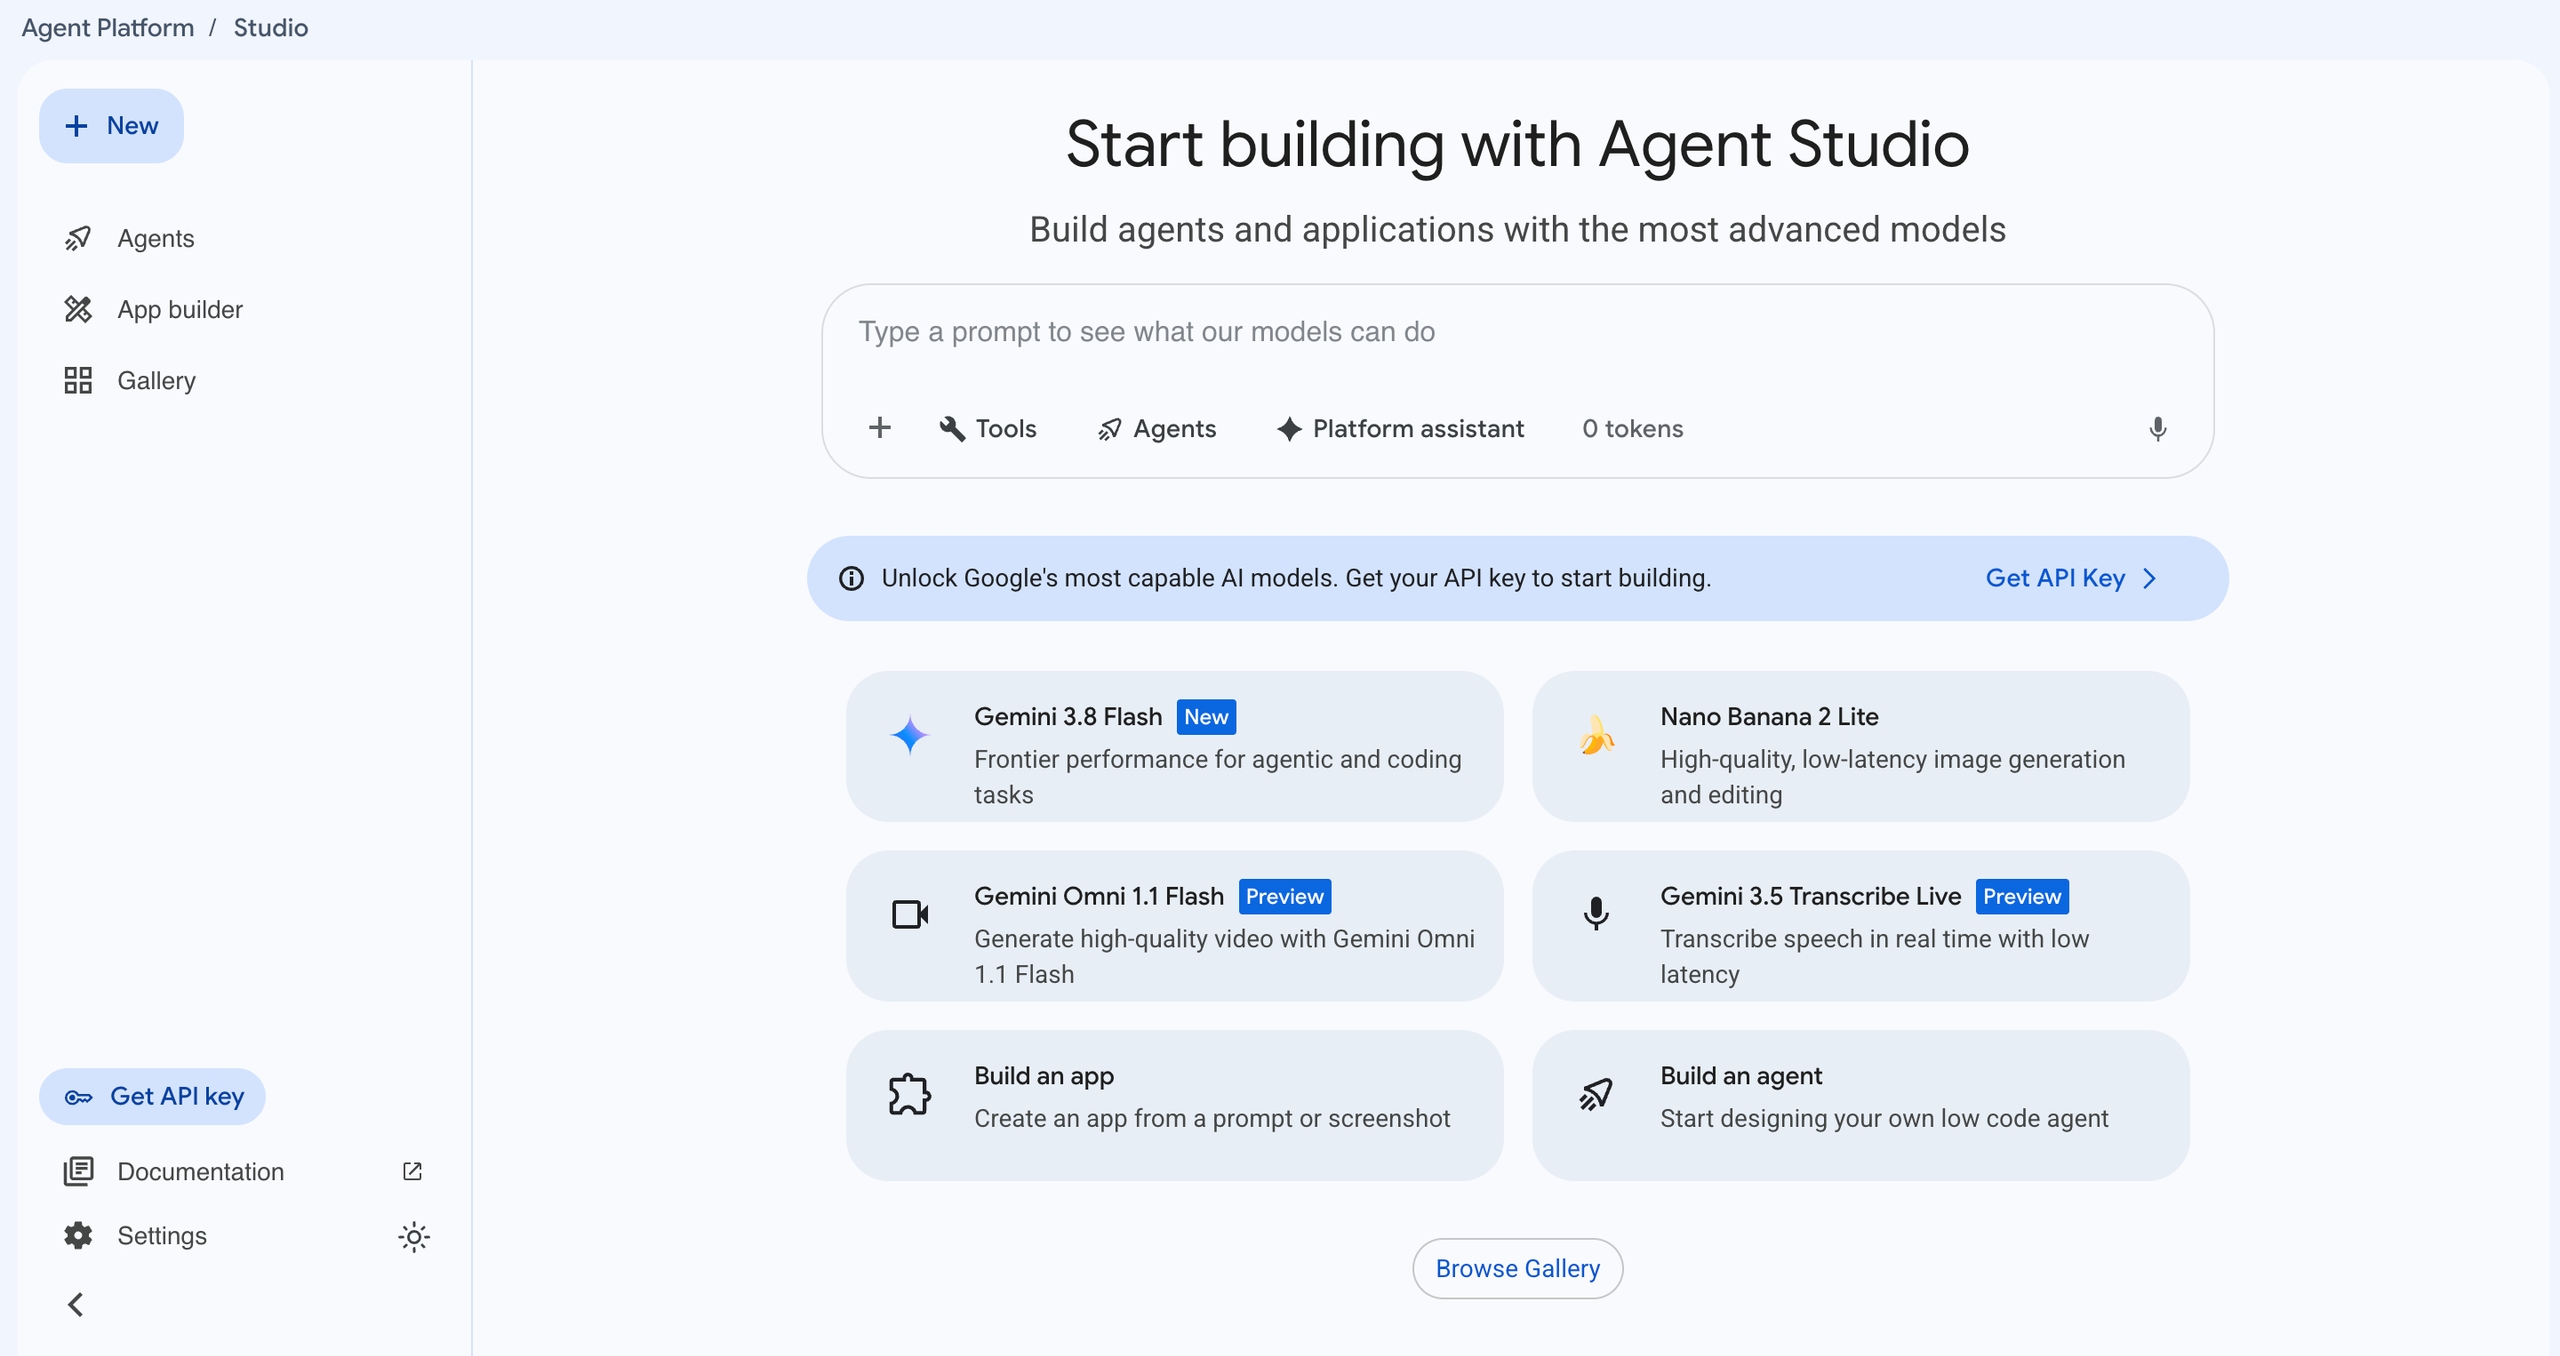
Agent Studio on GCP lists Gemini 3.8 Flash
Teams wiring up agents in Google Cloud’s Agent Studio can now pick Gemini 3.8 Flash, per a post flagging the listing. It’s pitched at coding problems, web research and application testing.
Related stories
- One of 225 Anthropic-linked CVEs actually got used
- Held-back Mythos 5 now scans enterprise code
- Irregular CEO blames human error for AI agent test hacks
- OpenAI puts live alarms on its agents after Medicare hack
- OpenAI and Anthropic probe tens of thousands of AI misfires
- Researchers used Claude to reach OpenAI’s internal code
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.