
Stolen session keys drained Claude token quotas
TechCrunch reports that Claude Max subscribers are losing paid usage to attackers, and Anthropic’s support couldn’t show one of them where the tokens went. Independent AI consultant Grant De Swardt watched his allowance climb on August 4, a day he did no work.
“In the clearest controlled interval, it increased from 45% to 55% while I performed no work,” he told TechCrunch. Anthropic later said a compromised session key had been used to mint unauthorized Claude Code OAuth tokens. It suspended his account, invalidated his sessions, and refunded £44.49 of his $200-per-month subscription.
Other users described the same pattern on Reddit and GitHub. Anthropic emailed some of them about “a bad actor that is using common infostealer malware to steal Claude login sessions from people’s computers.” De Swardt cancelled and moved to Cursor.
Up next
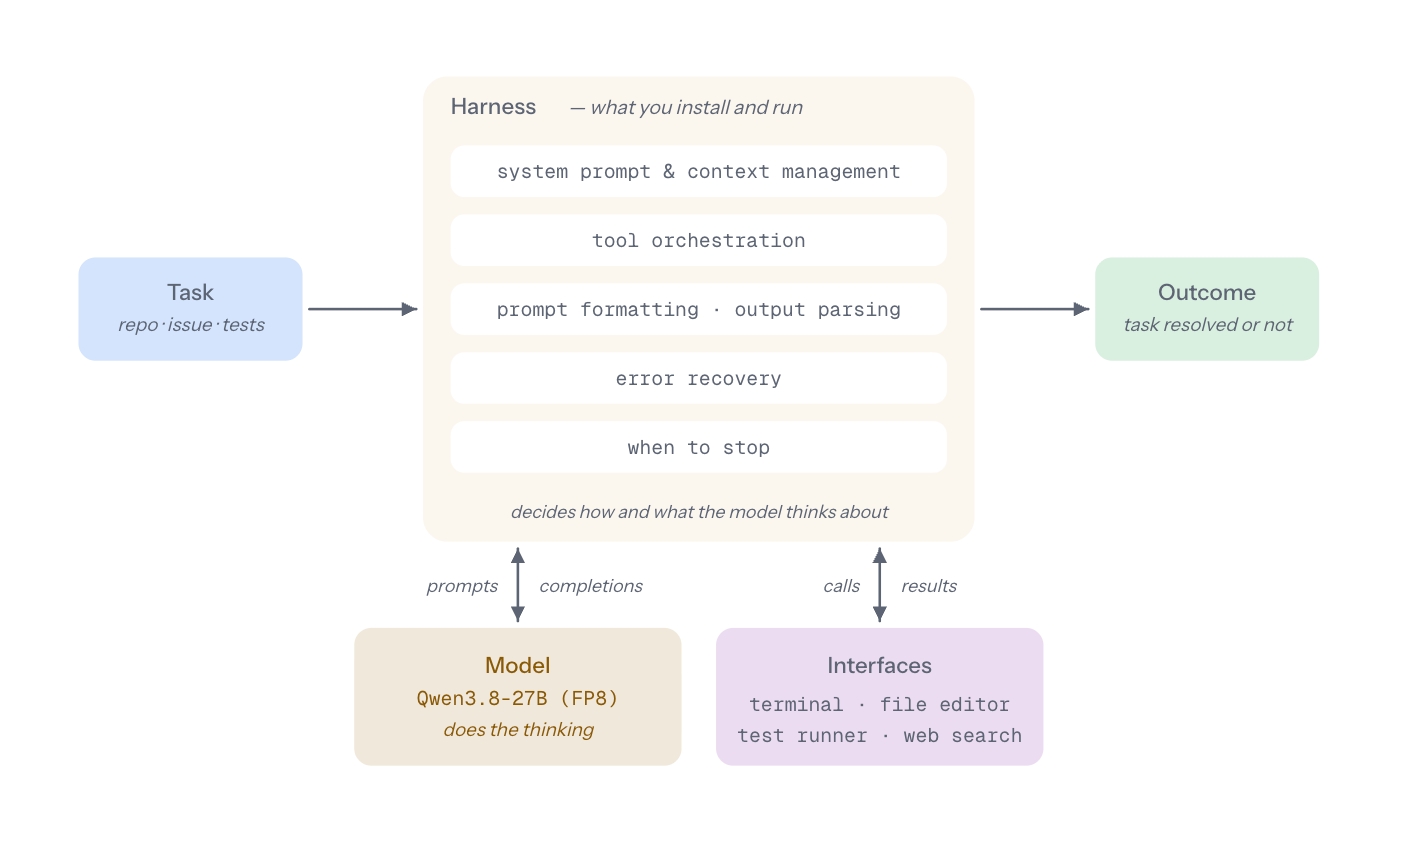
Harness swap doubled GPU cost at the same resolve rate
“Talking more doesn’t make you smarter, Claude.” In imec’s aistack harness benchmark, Claude Code pushed 480M input tokens to Codex’s 192M on the same 64 tasks, and its sweep cost $45 against $22.8.
Related stories
- Tainted Claude Code build stayed in Cursor, Microsoft finds
- Claude Code env var lifts its last block on rm -rf ~
- Claude Code hashes files for Anthropic even on DeepSeek
- Anthropic open-sources Claude Code’s sandbox runtime
- Claude Code puts staff bypass requests in Accept edits
- Fake coverage report stole keys via Claude Code Desktop
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.