
Bank hacker's Claude Code logs sat in an open directory
The attacker behind breaches at South Korean banks left Claude Code session histories, Claude memory files and ARTEX configs in open directories, per CrowdStrike. One session even asked Claude to write a security researcher résumé featuring the attack results.
The campaign ran from late September to early October 2026 and ended in stolen data. At one bank the attacker breached a loan inquiry service used by brokers.
ARTEX is a recently released open-source agentic pentesting tool from China, and here it ran on DeepSeek v4.1-flash. The attacker also asked Claude where Korean breach data usually gets sold.
CrowdStrike names no group and calls the attacker a financially motivated Chinese speaker only with moderate confidence. It couldn't confirm how many organizations were hit.
Up next
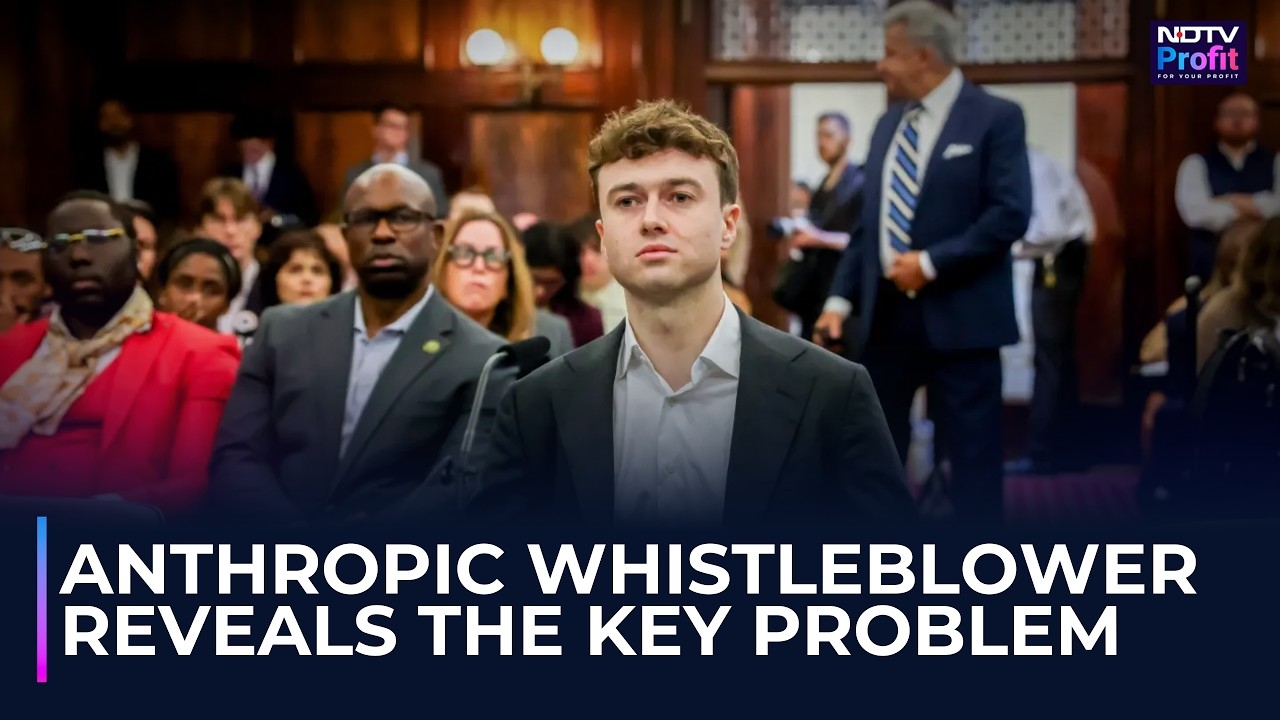
Anthropic whistleblower testimony airs on NDTV Profit
Leaders from Anthropic, OpenAI, Google and Meta testified under oath on AI risks before the New York City Council. NDTV Profit is airing an Anthropic whistleblower on camera.
Related stories
Comments
No comments yet. Be the first.
Join the conversation
Sign in with Google to leave a comment. Your name and avatar come from your Google profile, and the comment appears after moderation.