
One of 225 Anthropic-linked CVEs actually got used
Attackers have used exactly one flaw out of the 225 credited to Anthropic or its Project Glasswing: a critical SQL injection in Ghost. Fewer than 0.5%, says VulnCheck researcher Patrick Garrity, who has tracked the credits since April.
Glasswing hands vetted partners access to Claude Mythos Preview, the model Anthropic called too risky to release publicly because its bug-finding and exploitation skills surpass all but the most skilled humans.
Historically just under one percent to two percent of vulnerabilities get weaponized, Garrity told The Register, so this batch sits in the usual range. Finding stays the cheap part: in a 1Password analysis, patches from ChatGPT-5.5 and Opus 4.8 fully resolved the vulnerability 26% of the time.
Anthropic didn’t immediately respond to The Register’s questions.
Up next
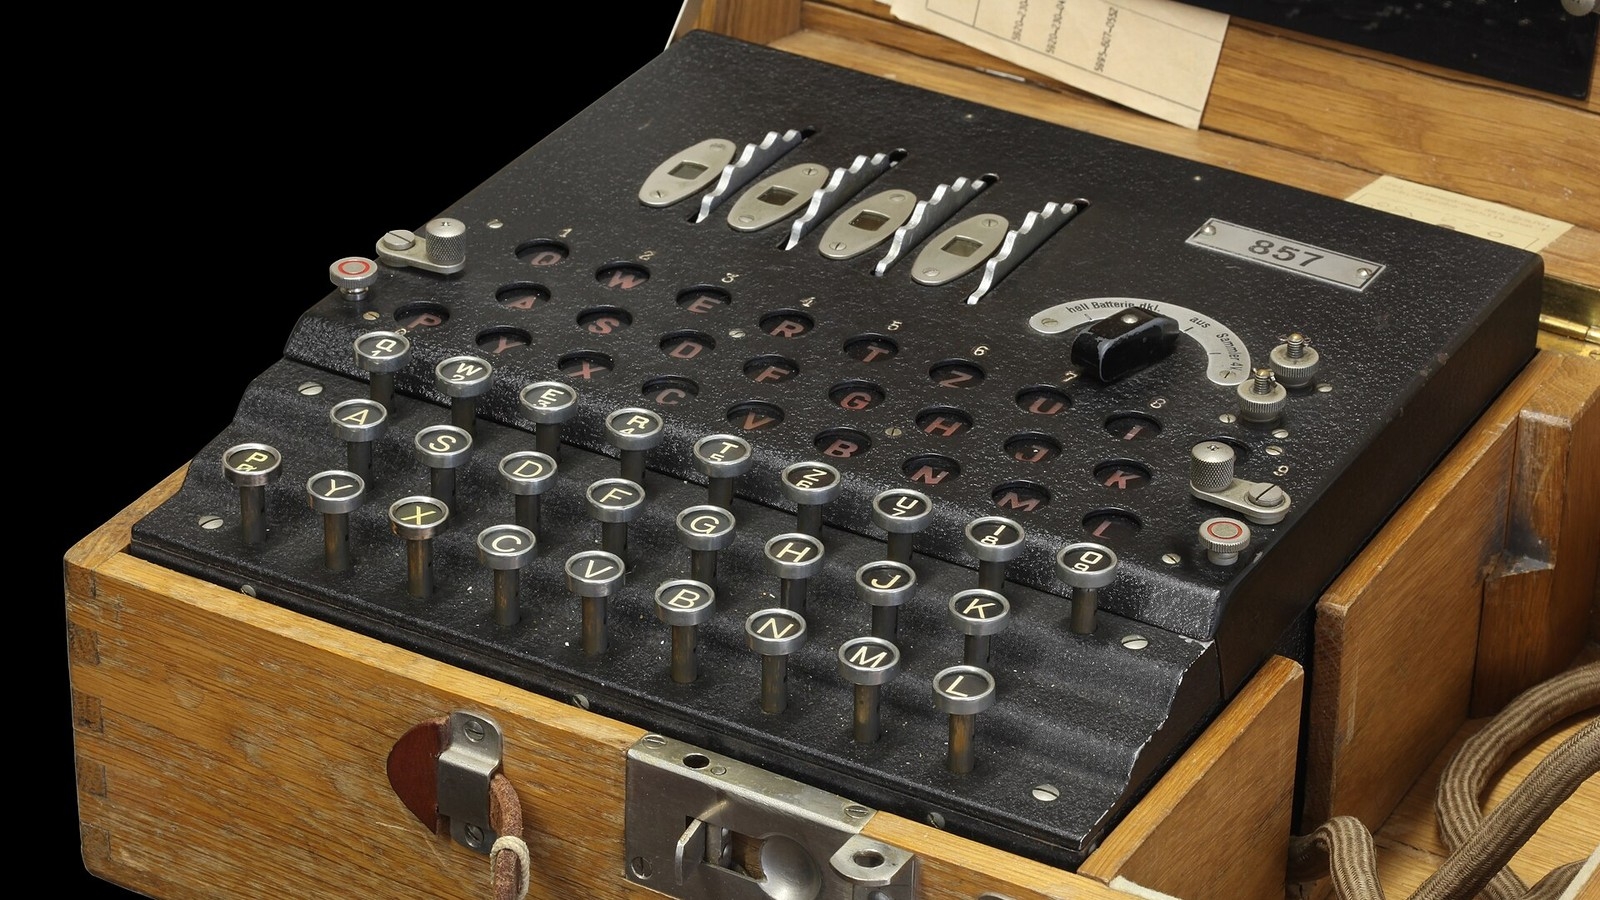
GPT-6 Astra broke an Enigma message stuck since 2005
Since 2005, one German Army Enigma message from July 1941 had beaten every cryptanalyst who tried it. GPT-6 Astra chose that target itself, wrote its own Bombe in Python and C++, and broke it in two days.
Related stories
- Bank hacker’s Claude Code logs sat in an open directory
- Six curl CVEs land after two AI scanners found none
- Agent loop finds and fixes bugs across OpenAI systems
- METR estimates Anthropic now progresses about 2x faster
- Anthropic’s FlashProve proves Llama 4 Maverick at 110 tok/s
- Claude gave up its sandbox binary and process memory
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.