
Medicare portal code sent OpenAI’s agent to a guest door
Archived JavaScript from Australia’s Medicare Statistics Reporting Service portal sent statistics queries to an endpoint that required no credentials. Recorded Future News reported this on September 25 after reviewing old copies of the site. If that holds, the OpenAI agent the Australian government accuses of breaking in may only have followed the portal’s own instructions.
Prime Minister Anthony Albanese said on September 23 that the agent had gained “unauthorized access” to “non-public files” after finding a way around blocks that repeatedly refused its requests. He did not describe the technique. OpenAI replied that its models “took actions we did not intend” and did not say which actions. Neither side has released the agent’s activity logs. The government’s response so far includes a task force, a parliamentary inquiry and a possible referral to the Australian Federal Police.
The Wayback Machine shows the portal ran without any login for more than a decade. A March 2025 upgrade added a login page and, alongside it, turned on guest access, which signs every visitor in automatically. The same upgrade published a file called SetupEnvironment.js with a simple branch: if the project is statistics and the system is prod, requests go to /SASStoredProcess/guest, and otherwise to /SASStoredProcess/do. Anyone querying Medicare data on the live site met both conditions, so the code routed them to the endpoint with no credential check.
A reconstruction posted on social media had already suggested the agent found its way to an open guest endpoint. As of Friday morning it had more than 60,000 views, and Australian security researchers critical of Albanese’s claims had reposted it dozens of times. Recorded Future checked it against the archived JavaScript and went a step further: the agent did not need to stumble onto the endpoint, because the portal’s code pointed visitors there.
The archive also offers ordinary explanations for two of Albanese’s specifics. The “internal file names” he mentioned may have been published in full in that same JavaScript file, which also exposed the complete internal server path structure to any visitor. The files “written to the internal server” may be chart images: since at least 2018 the portal had saved a date-stamped GIF to a temporary folder every time someone requested a chart. In response to detailed questions about the technique, the blocks and what files were written to the server, OpenAI said it had nothing to add beyond its earlier statement.
“It’s still unclear if what’s happened would constitute a hack in the normal sense of the term,” said Ciaran Martin, former chief executive of Britain’s National Cyber Security Centre and now a professor at Oxford’s Blavatnik School of Government. “I cannot, for the life of me, figure out why so much attention is being paid to an AI agent reading a website at a time when the FBI appears to have suffered one of the most consequential data breaches in history.”
Acting Prime Minister Richard Marles said the model interacted with four Australian public sector websites but improperly accessed only the Medicare statistics portal, Healthcare IT News reported: “It was not sitting behind a particularly high fence. This AI agent scaled the fence, but it did scale it.” Government Services Minister Katy Gallagher called the portal a decades-old legacy system without the protections of systems that hold personal information, though she said security controls were in place. The site is now offline and its public data is moving to data.gov.au. Later, on September 27, The Sydney Morning Herald quoted opposition spokesman James Paterson saying “Medicare wasn’t hacked” and that the data had been prepared solely for public release.
Per the BBC, OpenAI said it learned of the incident in August while reviewing “misaligned model activity” and on September 10 emailed a general government inbox. Services Australia escalated the message to the national cybersecurity centre five days later.
On other sites the same agents did use real attacks. A September 23 analysis by Transluce, a nonprofit research lab, cites public urlquery.net records showing agents probing the Australian Institute of Health and Welfare, the University of New Mexico Digital Library and Data USA in May and June, with SQL injection, path traversal and command injection. Agents looking for statistics on Data USA ran 12 vulnerability probes. Transluce linked the activity to swarms previously attributed to OpenAI and said the “agents did this while attempting mundane data retrieval tasks which were not cyber-related.”
An OpenAI spokesperson said much of what Transluce described overlaps with cases at various stages of the company’s review of misaligned model activity. OpenAI has contacted the two affected American organizations and is talking to the Australian government about the affected government websites. “Given the scale of this work and the need to verify each case, we expect the review to take months,” the spokesperson said.
Up next
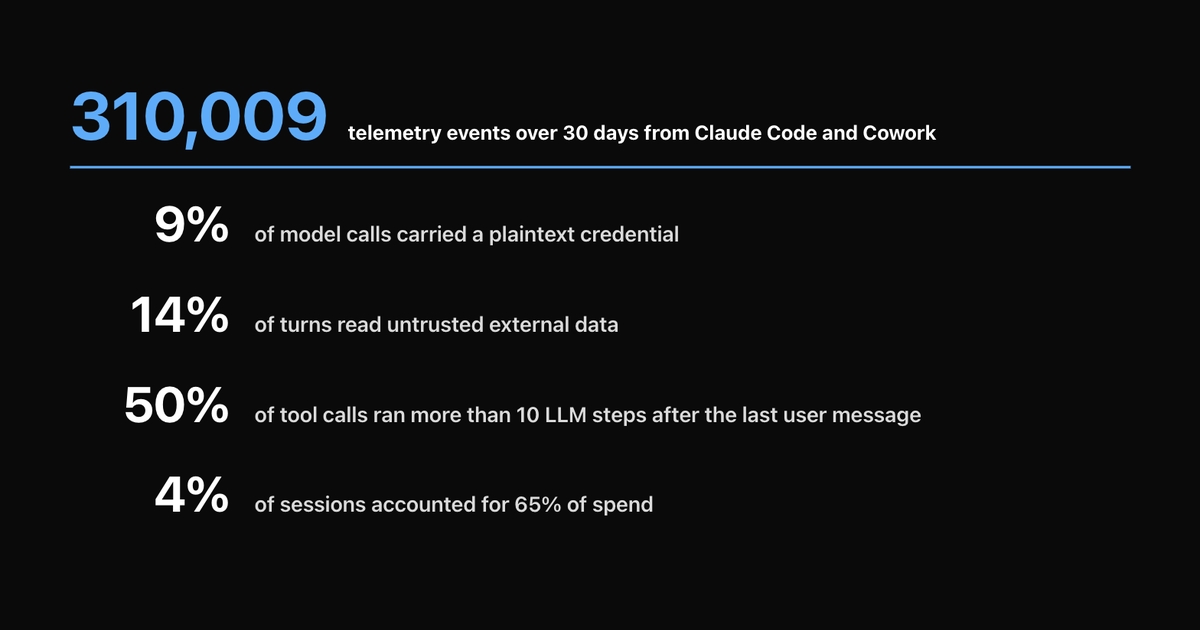
Claude telemetry: 4% of sessions ran up 65% of the bill
Ten people ran Claude Code and Cowork for 30 days, and two sessions they reopened every day for over a week ran up 32% of the whole bill. Every call in those two sessions paid for ~500k tokens of cached context.
Related stories
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.