
Claude Code puts staff bypass requests in Accept edits
Employee sessions that ask Claude Code for bypass mode, where the agent skips permission prompts, start in Accept edits instead, according to RuntimeWire’s October 18 inspection of the publicly distributed Claude Code JavaScript. The behavior sits in a separate session-start handler for employee accounts.
The same client keeps two error paths apart. One refuses staff sessions with unapproved security controls, the other flags outdated clients. RuntimeWire traced the API-error parser to its staff-facing messages and preserved the files’ bytes and SHA-256 hashes.
The evidence is the client code alone. No live API response was observed, and RuntimeWire says it couldn’t independently reproduce the finding.
Up next
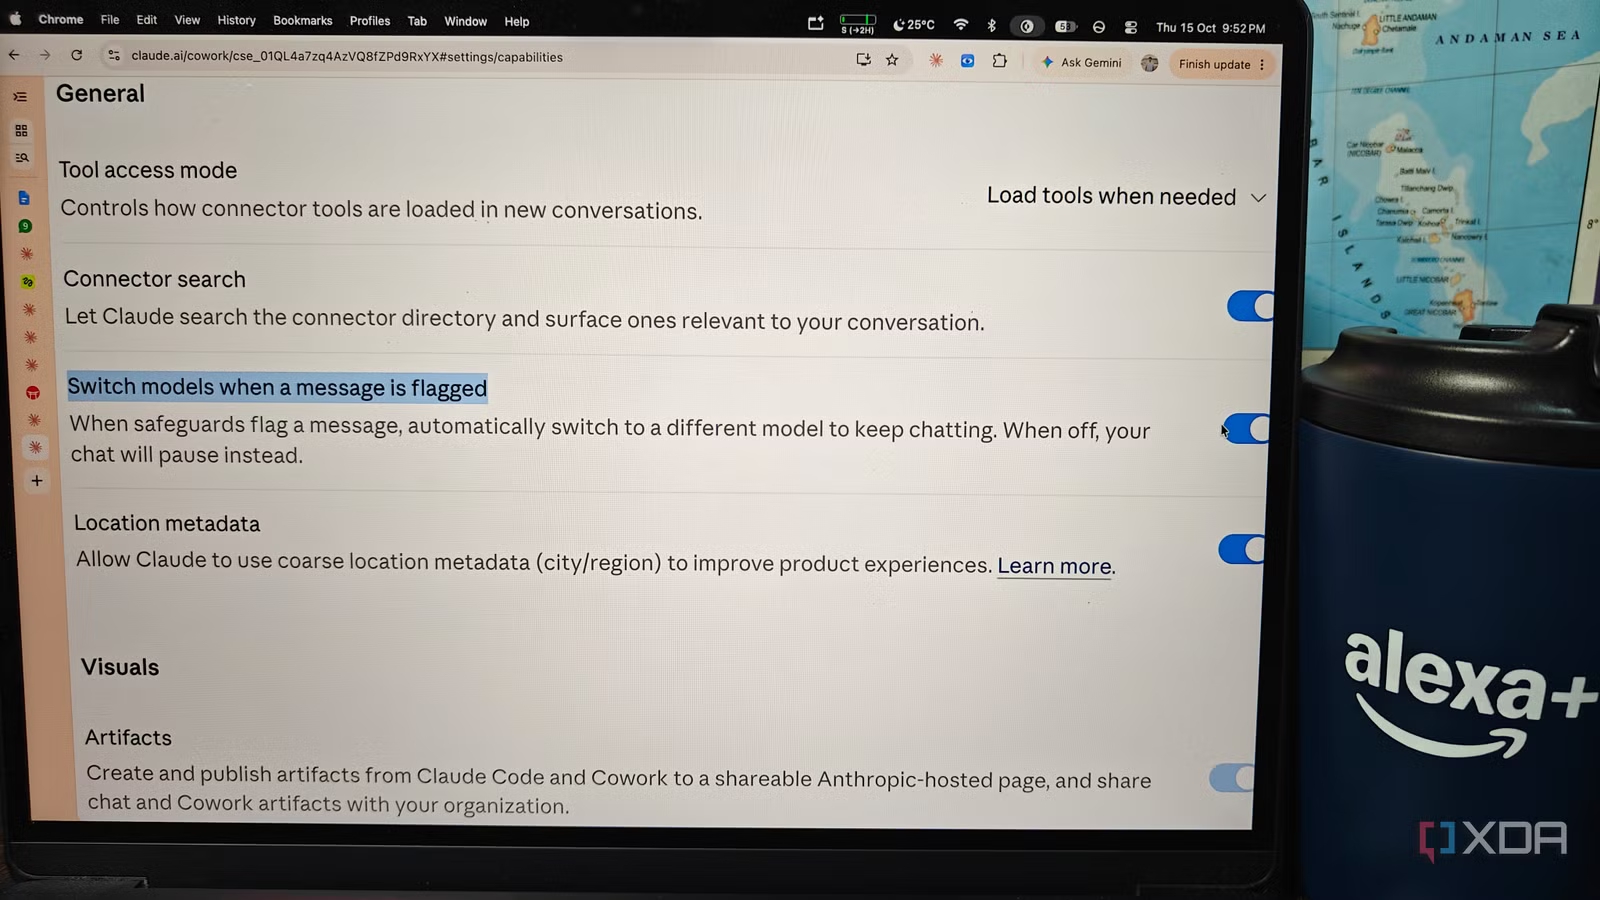
Opus 5.5 hands flagged security chats to Opus 4.8
Flagged Opus 5.5 chats move to Opus 4.8 and stay there. In Anthropic’s Sonnet test of that same fallback, 12.01% of rerouted requests got compromised, vs 4 of 5,901 on the newer model. Would you let a flagged agent run fall back to an older model, or make it stop?
Related stories
- Fake coverage report stole keys via Claude Code Desktop
- Bank hacker’s Claude Code logs sat in an open directory
- A poisoned repo escaped Claude Code’s sandbox in one message
- Stolen session keys drained Claude token quotas
- MCP OAuth tokens sit in plaintext on Linux
- Auto Mode break in Claude Code still open
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.