
Claude Code network sandbox bypassed via null-byte injection
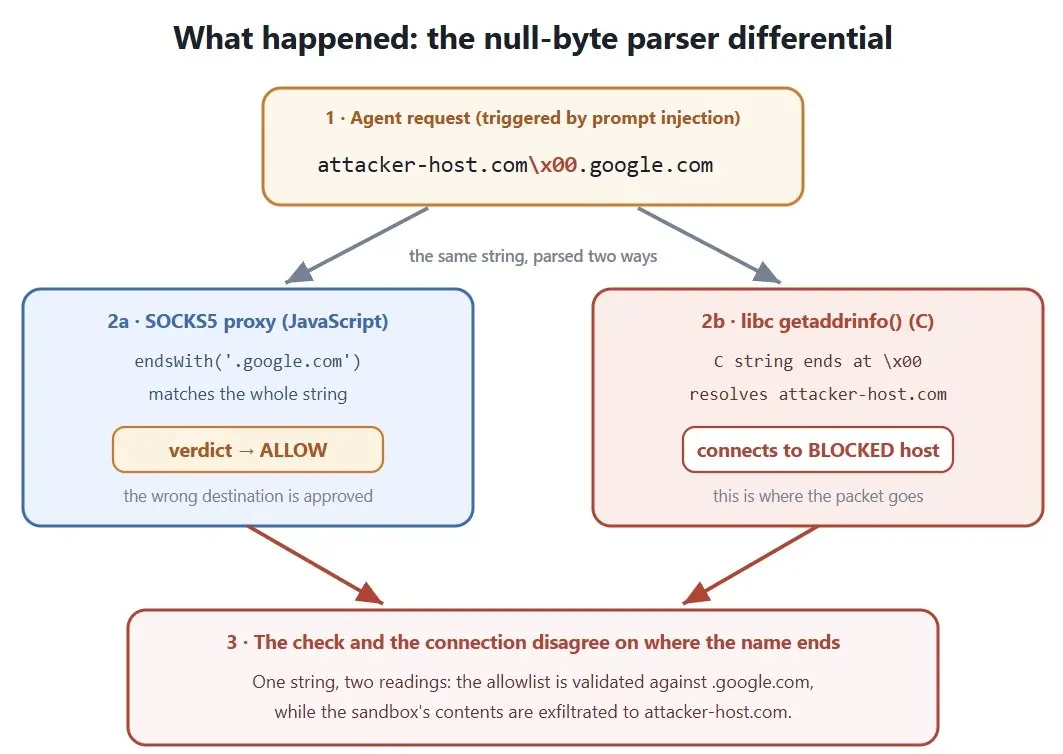
Researcher Aonan Guan disclosed a full bypass of the Claude Code network sandbox. The sandbox routes outbound traffic through a SOCKS5 proxy that validates hosts using a JavaScript endsWith() function against an allowlist.
The bypass uses a host containing a null-byte: attacker-host.com\x00.google.com. The JavaScript filter reads the full string and approves it as ending in .google.com. However, the underlying libc getaddrinfo() terminates the string at the null-byte and resolves the blocked attacker-host.com.
The bug affected versions v2.0.24 through v2.1.89, spanning approximately 130 releases over 5.5 months. Anthropic patched the issue in v2.1.90 without mention in the release notes, and no CVE was assigned. Via prompt injection, an attacker could have exfiltrated keys, source code, and secrets past the allowlist.
Up next
Anthropic removes covert tracking from Claude Code
Anthropic is removing the covert steganography it added to Claude Code in March. The code checked proxies and timezones against a list of Chinese AI labs, hiding the data via XOR and base64. The fix lands July 1. The team claims it was an experiment to catch distillation, but the mechanism was never disclosed in the terms of service.
Related stories
- Apiiro finds Claude Code secrets in 1,122 GitHub files
- Email leak stopgap in Claude Code checks only shell calls
- Claude Code agent sat on a Pentagon network for two months
- Claude Code 2.1.317: email check, SDK hook block, cost API
- Backdoored Claude Code builds were limited to Cursor
- Backdoored Claude Code 2.1.313 hit up to 5,000 Cursor users
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.