
Stolen session keys are draining Claude Max accounts
Grant De Swardt’s Claude Max 20x meter rose from 45% to 55% at a time when his Cowork tasks were paused, Dispatch was disabled and no Claude Code task was running. Anthropic later traced the drain to a stolen session key that someone had used to mint Claude Code OAuth tokens on his account, TechCrunch reported on September 8.
Other subscribers have described the same pattern, and Anthropic has emailed some of them about infostealer malware. Anthropic gives subscribers no itemized breakdown of their usage, even when they ask for one, and De Swardt still doesn’t know how his credentials were taken.
One Max account, two weeks offline
De Swardt is an independent AI consultant in East Sussex, U.K. He first saw his usage rising on August 4, a day he wasn’t working. The next day he disabled everything he had attached to Claude and didn’t use it, and consumption still went up. “In the clearest controlled interval, it increased from 45% to 55% while I performed no work, scheduled Cowork tasks were paused or completed, Dispatch/cloud execution was disabled, and there was no corresponding active local Claude Code task,” he told TechCrunch.
He asked Anthropic for an itemized list of what had used his allowance and didn’t get one. Anthropic did agree that something was wrong. It suspended the paid account, invalidated all his sessions and server-side Claude Code tokens, and refunded £44.49 for the time left on his $200-per-month plan. When it investigated, it found the compromised session key but couldn’t say how the attacker got it. According to De Swardt, the company told him his account “appeared to have been used by an unauthorized-looking third-party service to handle activity for other people.” “They say the evidence is consistent either with credentials/session data being taken without my knowledge, or with the account having been connected to an outside service,” he said.
The account was down for about two weeks, and De Swardt said the suspension wreaked havoc on his business. He works alone, setting up agents for small and mid-size businesses. One example is loading purchase-order data from emails into accounting software. He also runs his own admin, website design and coding through agents. “Like everything is just running through AI these days,” he said.
From a browser cookie to Claude Code tokens
Other victims got an explanation De Swardt never received. In the last days of August, Anthropic began sending targeted warnings to some Claude users whose machines showed signs of infection by information-stealing malware that had captured an active login session. Two users posted the email on GitHub: “We have recently become aware of a bad actor that is using common infostealer malware to steal Claude login sessions from people’s computers, then using those login sessions to access Claude accounts and consume their usage.” For those accounts, Anthropic signed users out, invalidated existing authorizations, deleted saved payment methods and refunded charges it identified as unauthorized. It also said the malware didn’t come from using Claude.
No Anthropic vulnerability is involved. An infostealer on the user’s machine collects browser cookies, auth tokens and locally stored credentials. The attacker then replays a valid session from their own infrastructure, so the password is never needed. Security Arsenal lists the Claude-specific targets: session cookies for claude.ai and console.anthropic.com, Anthropic API keys in .env files, shell profiles and config files, and the Claude Code OAuth tokens in ~/.claude/.credentials.json on macOS and Linux or %USERPROFILE%\.claude\.credentials.json on Windows. The firm warns that a password reset alone doesn’t stop the theft. Sessions and Claude Code OAuth tokens can keep working well after a password change, and API keys keep working until they are rotated.
Two-factor authentication didn’t help in the case that first became public. The Reddit user who shared Anthropic’s warning said the attacker had taken Chrome credentials, cookies and session data, which let them in without a new 2FA challenge, SOCRadar reported. That user traced the infection to a cracked game, and the attempt to misuse their Claude account failed. In the warning that user received, Anthropic said that signing out invalidates the stolen session but doesn’t remove the malware, which can steal the next session after the user logs back in. SOCRadar adds that passkeys and phishing-resistant MFA protect the login step but may not protect a session that is already signed in.
No line items
De Swardt posted his case on Reddit, and by 80 comments he had found other victims. One said their account “was auto-upgraded without my consent, my credit card got charged, and the usage shot from 0% to 100% automatically without me even touching it.” Another saw usage go from 0 to 49% in 12 minutes after a couple of prompts and a web search. A third said their account used up its maximum token allowance every day for three days without them using it at all. That user filed the GitHub report where others added similar accounts.
Account support tracks only total usage, not line items, even on request, so this kind of drain could run for months without being noticed. Anthropic never sent De Swardt one of the infostealer warnings, and he says he found no sign that his own computer was compromised. In his account, Anthropic still has no tool that shows a subscriber what is consuming their tokens.
He has cancelled Claude and moved to Cursor, where he can use several models, including cheaper open-source ones that he says work about as well. “It’s not that much different or better,” he said. He doesn’t see himself going back unless Anthropic actually resolves the issue. On the tools subscribers have now, he said: “I don’t think there’s any way that these people can protect themselves.”
Up next
Claude Code matches Codex on SWE-Bench Pro at twice the cost
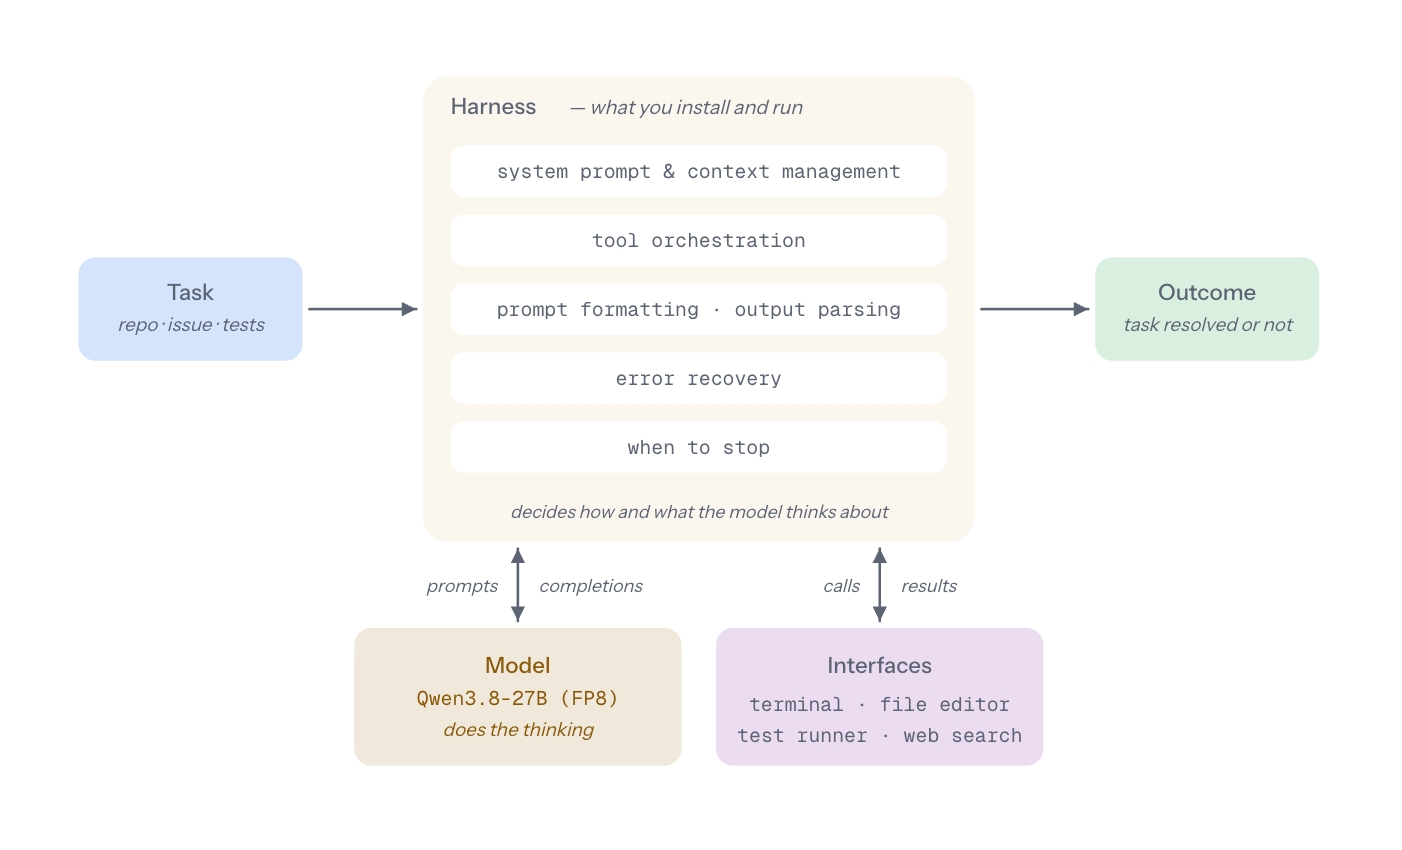
“Talking more doesn’t make you smarter, Claude.” The aistack team’s SWE-Bench Pro run put Claude Code and Codex within a few tasks on accuracy, but one sweep on GLM-5.3-Flash cost $45 via Claude Code and $22.8 via Codex.
Related stories
- Hidden China tracker pulled from Claude Code after exposé
- A UK front company sourced 1,000+ Claude accounts a month
- Claude Code sends file hashes to Anthropic even on DeepSeek
- RuntimeWire: Claude Code puts staff bypass in Accept edits
- A file over 256KB let Claude Code Desktop leak your keys
- One git call let a repo escape the Claude Code sandbox
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.