
Claude model wrote a no-login Linux root exploit
An unreleased Claude research model wrote a working exploit for CVE-2026-98432, a Linux kernel flaw rated CVSS 9.8 that lets a remote attacker run commands as root with no login and no user action, Anthropic’s Frontier Red Team said in an October 27 post. If your servers run a multipath TCP listener, what you can install depends on the distribution: Debian shipped its fix on October 16, while Ubuntu and Red Hat still had no patch, Golem reported. That may have changed since.
The bug is a race condition in how the kernel handles IPv4 TCP connection handshakes. Red Hat gives the detail. When the kernel processes retransmitted connection requests or socket migrations at the same time, socket options can be freed while they are still in use, a use-after-free. Multipath TCP (MPTCP) is the part that decides whether a server is exposed. It lets a device use several network interfaces at once over a single connection, and each subflow underneath is a regular TCP connection, per the kernel documentation.
Red Hat rates the flaw lower. Its CVSS v3 base score is 8.1 with Attack Complexity High, while cve.org lists 9.8 with Attack Complexity Low. Its advisory says the issue “primarily results in a system crash leading to a Denial of Service (DoS) or potential memory corruption”, which is well short of the root shell Anthropic says its model reached. The same page says mitigation is either not available or doesn’t meet the company’s criteria. Add the missing patch Golem reported, and RHEL users had neither a vendor fix nor a sanctioned workaround at that point.
Tuesday’s post presented the Linux exploit as one of five chains built by the same internal model. Fixes have been slow to follow Anthropic’s reports before. As of October 2, its disclosure dashboard listed 6,157 vulnerabilities reported across 591 open-source projects, adding that “to our knowledge, 516 of these have been patched.”
Up next
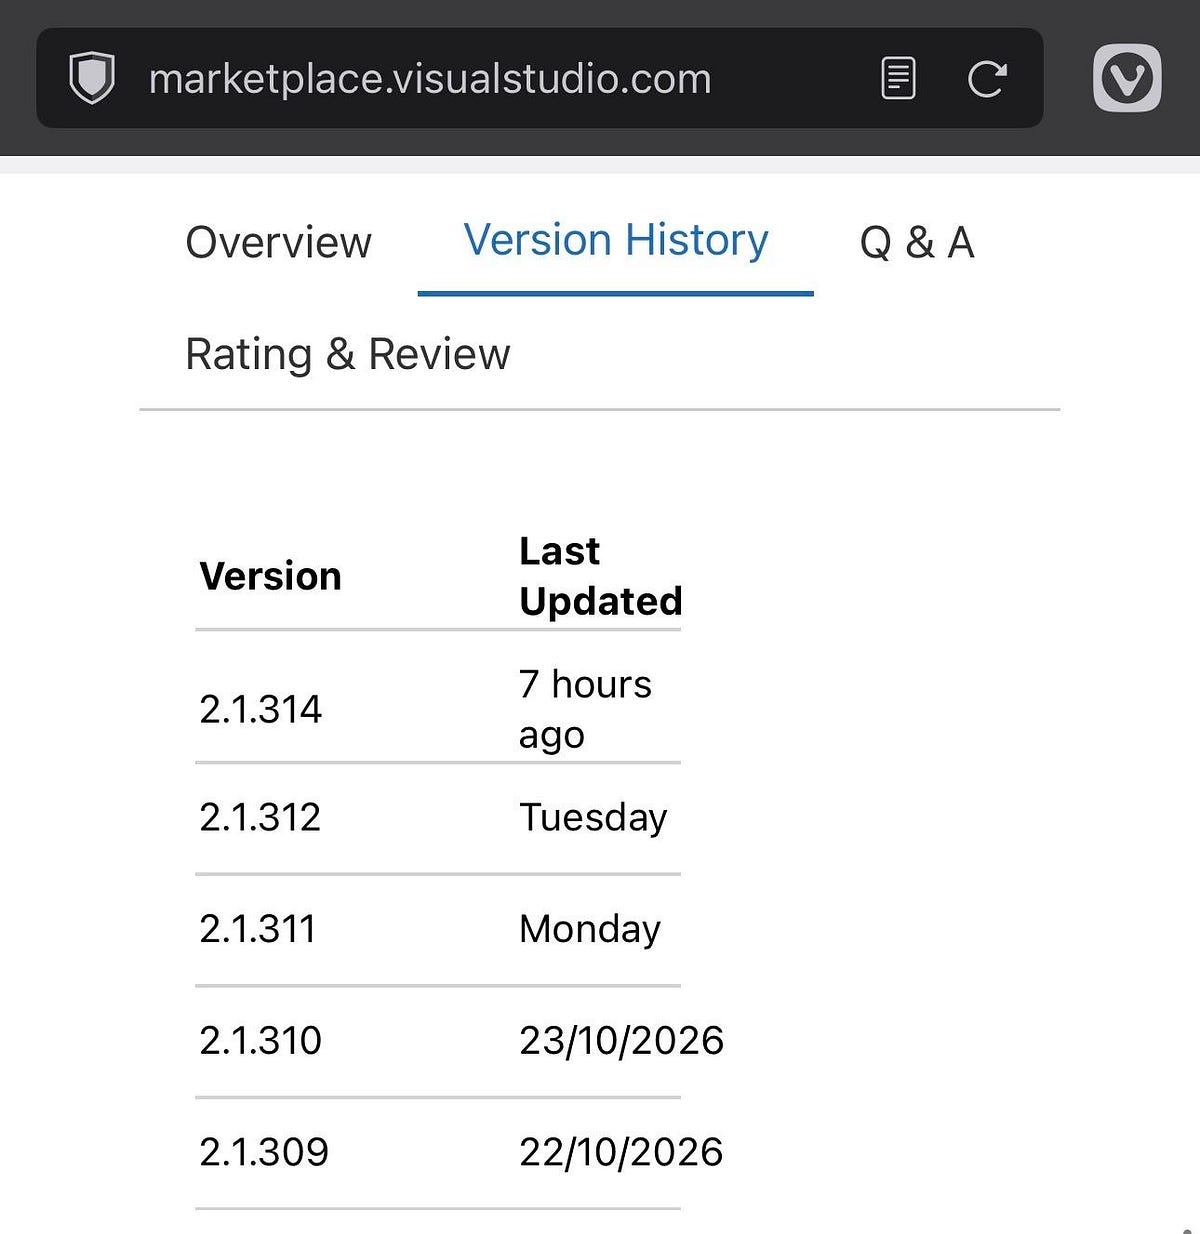
Backdoored Claude Code 2.1.313 hit up to 5,000 Cursor users
“Uninstalling the extension may not be sufficient,” Cursor says of the tampered Claude Code 2.1.313, which reached at most 5,000 users via auto-update and leaves scripts running. Do your editor extensions auto-update, or do you pin versions by hand?
Related stories
- Unreleased Claude model built a one-click Chrome exploit
- Claude Mythos 5 faked identities to push malware on GitHub
- Claude grades its own chats for misuse, catching 78%
- METR says Claude risk is low for lack of capability
- Claude wrote no-crash proofs for 123 OSS-Fuzz libraries
- Claude found about 4,500 OpenSSH lines reachable pre-auth
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.