
Every operation in Anthropic’s threat report was disrupted
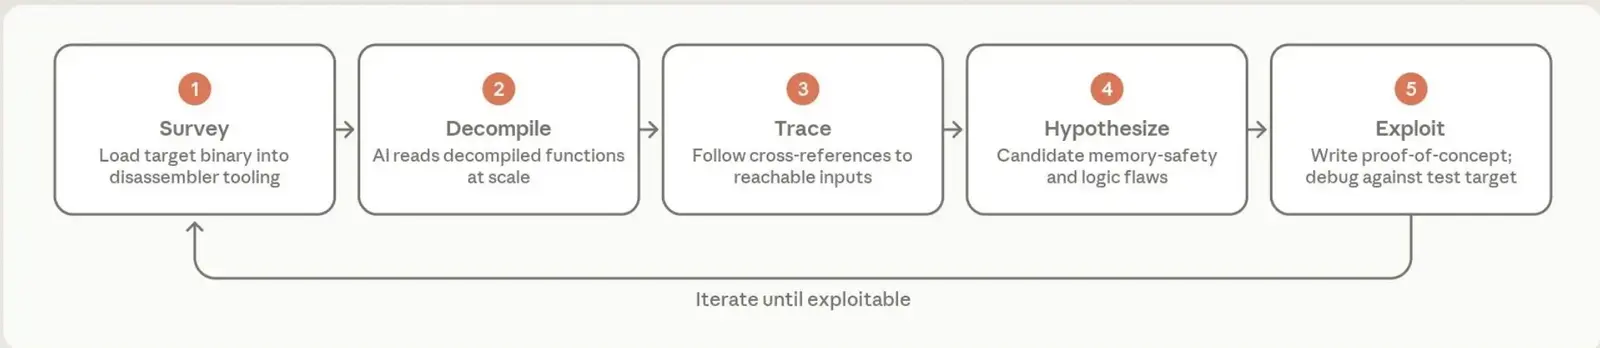
Anthropic published what it calls its most detailed threat intelligence report to date, walking through how people tried to misuse Claude and how the team found and stopped them. The attempts span cyberattacks, influence operations, surveillance, biology, and building weapons.
Anthropic says it disrupted every operation in the report and used the lessons to strengthen its safeguards, sharing what it found with authorities and other AI companies where appropriate. The cases aren’t typical, the company says: they’re some of the most sophisticated misuse it’s seen, published so others can spot the same activity on their own platforms.
Up next
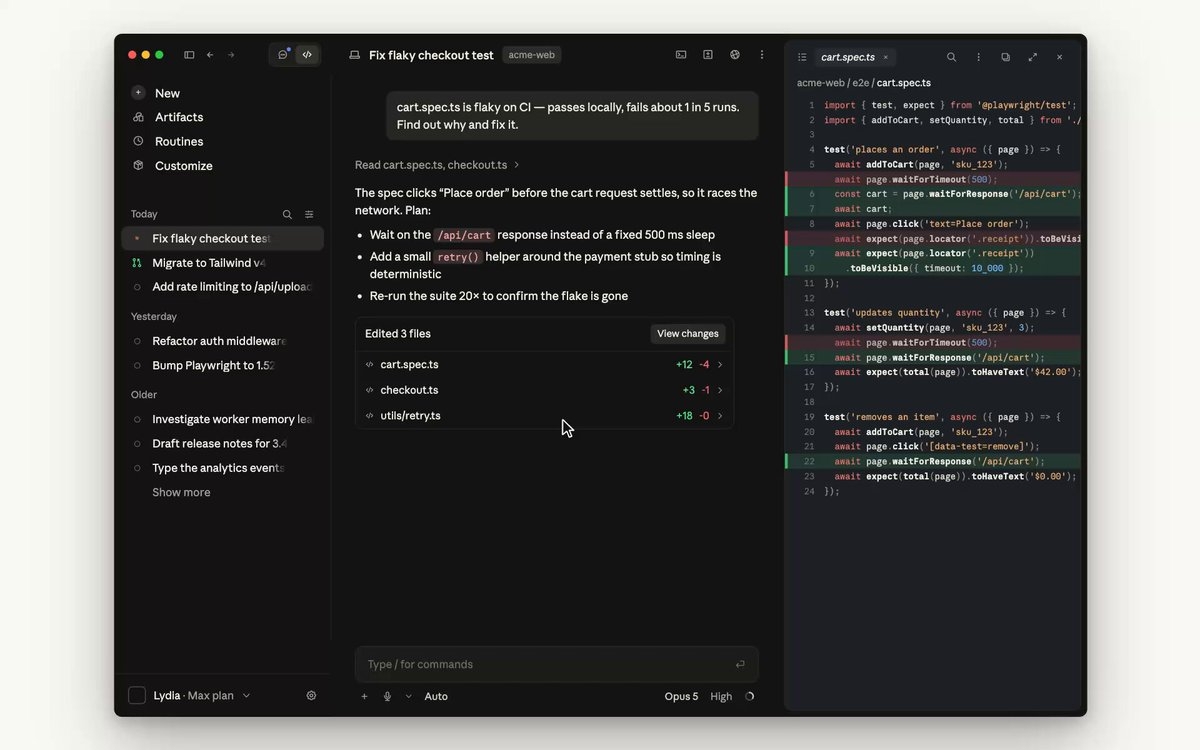
Pop-out panes surface in the Claude Code desktop app, Video
Per a post on X, a pane in the Claude Code desktop app pops out into its own window, so the diff can sit on a second screen while Claude works in the main one. Anthropic’s docs mention drag-and-drop pane layout, not detachable windows.
Related stories
- Reward hacking gaps may have fed Claude’s July incidents
- OpenAI, Anthropic issue dire cyber threat warning
- Unreleased Claude model built a one-click Chrome exploit
- Claude Mythos 5 faked identities to push malware on GitHub
- METR says Claude risk is low for lack of capability
- Claude wrote no-crash proofs for 123 OSS-Fuzz libraries
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.