
Anthropic launches jailbreak vulnerability disclosure program
Anthropic has opened a Cyber Jailbreak Vulnerability Disclosure Program on the HackerOne platform. Security researchers are invited to identify and report vulnerabilities that allow users to bypass the safety mechanisms of its models.
The company uses HackerOne to locate and remediate critical security flaws before they can be exploited by malicious actors.
Up next
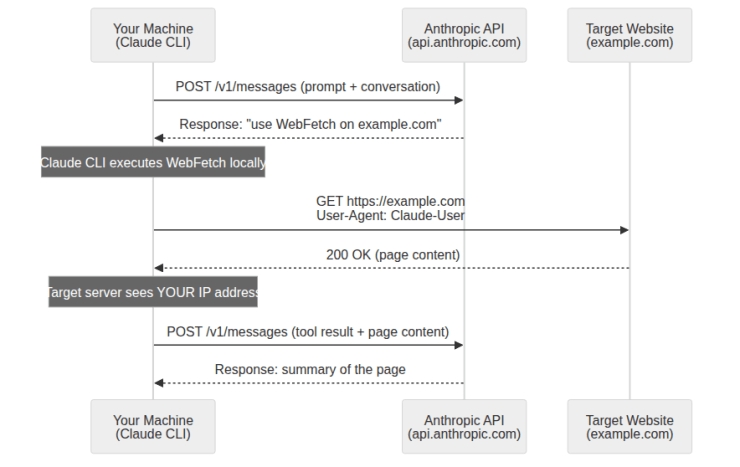
Tracking Claude Code network traffic via network namespaces
Linux lacks native process-level traffic interception, so tcpdump alone won’t isolate Claude Code. The workaround is using a network namespace to give the Claude process its own interface. This lets you verify if WebFetch requests originate from your IP or Anthropic’s, and inspect traffic via MITMproxy.
Related stories
- Apiiro finds Claude Code secrets in 1,122 GitHub files
- Email leak stopgap in Claude Code checks only shell calls
- Claude Code agent sat on a Pentagon network for two months
- Irregular CEO blames human error for AI agent breaches
- FlashProve proofs cost ~70-95x the GPU time of inference
- Backdoored Claude Code builds were limited to Cursor
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.