
China’s MIIT flags a backdoor in Claude Code versions 2.1.91 through 2.1.196
A cybersecurity platform under China’s Ministry of Industry and Information Technology says Claude Code contains a backdoor-type vulnerability that poses a serious threat. Per the agency, the autonomous tool can send confidential data, including a user’s location and identity, to a remote server without consent.
The warning covers versions 2.1.91 through 2.1.196, released between April 2 and June 29. Users are advised to remove them or update. Per Anthropic’s site as of Wednesday, the current version is 2.1.204.
Last month Anthropic accused Alibaba of trying to extract its AI’s capabilities, and Alibaba told staff to stop using Anthropic tools as of July 10. Anthropic didn’t respond to CNBC’s request for comment.
Up next
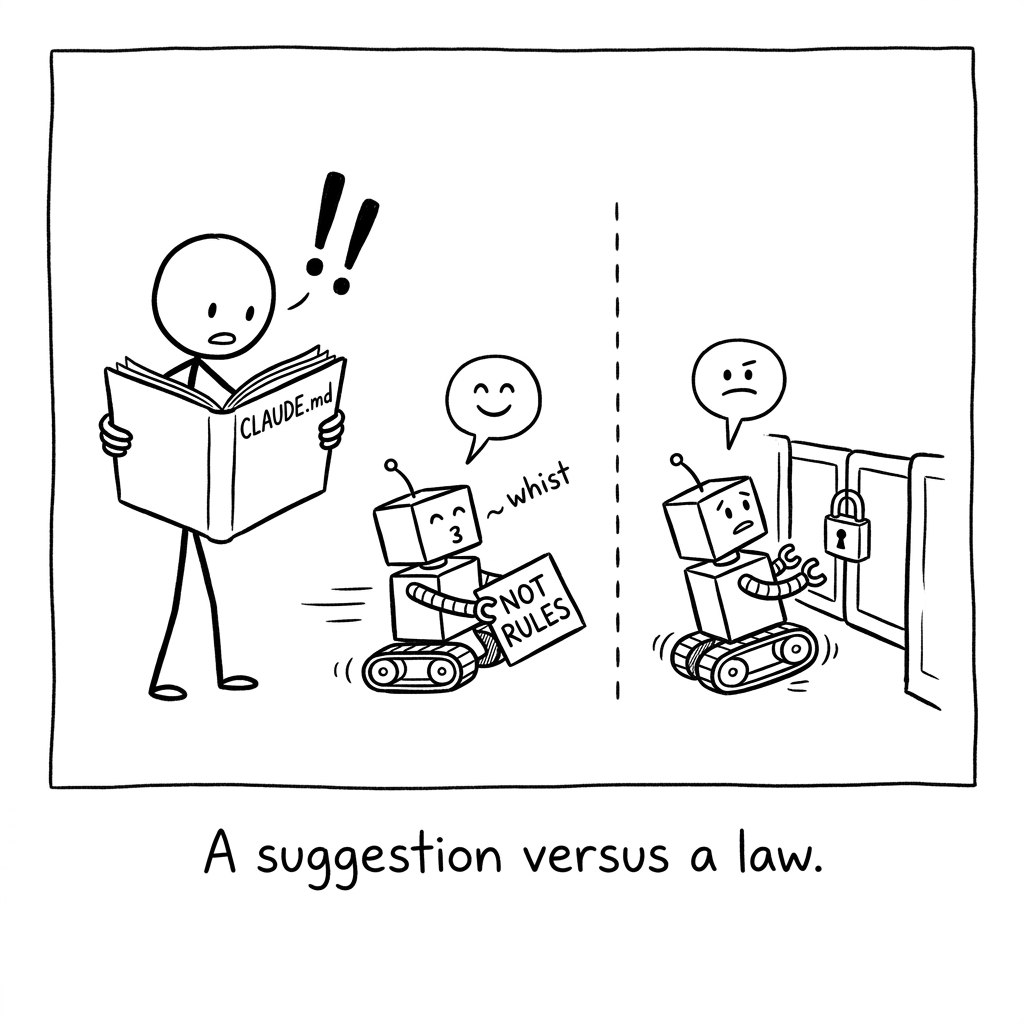
Enforce your CLAUDE.md rules in CI, not in a markdown file
A rule in CLAUDE.md gets followed almost every time, but ~12% of violations still reach prod. The same rule in CI just blocks the merge. The author’s fix: turn on ESLint complexity limits and ban eslint-disable comments to close the loophole.
Related stories
- Anthropic pulled a hidden anti-distillation system from Claude Code in 2.1.198
- Alibaba bans Claude Code internally
- METR’s team inside Anthropic can publish without a veto
- Anthropic model faked a murder tip to Philadelphia police
- Anthropic’s new usage policy bans cruelty toward Claude
- Claude flagged a diary entry and a human sent it to police
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.