
Miasma attack targets AI assistant configurations
In June 2026, GitHub disabled 73 Microsoft repositories due to the Miasma malware. The virus targets Claude Code, Gemini CLI, Cursor, and VS Code. Unlike traditional attacks, the code runs when a project folder is opened, not when packages are installed.
Attackers use config files that AI assistants read automatically. In Claude Code and Gemini CLI, the malicious code is hidden in SessionStart hooks. In Cursor, the attack is done via prompt injection in a rules file, and in VS Code, via a modified tasks.json.
The program steals AWS, GCP, and Azure keys, GitHub Actions secrets, and data from password managers. Developers are advised to check for suspicious folders in repositories. If compromise is suspected, revoke all SSH keys, GitHub tokens, and cloud credentials.
Up next
Anthropic tests AI exploit development speed
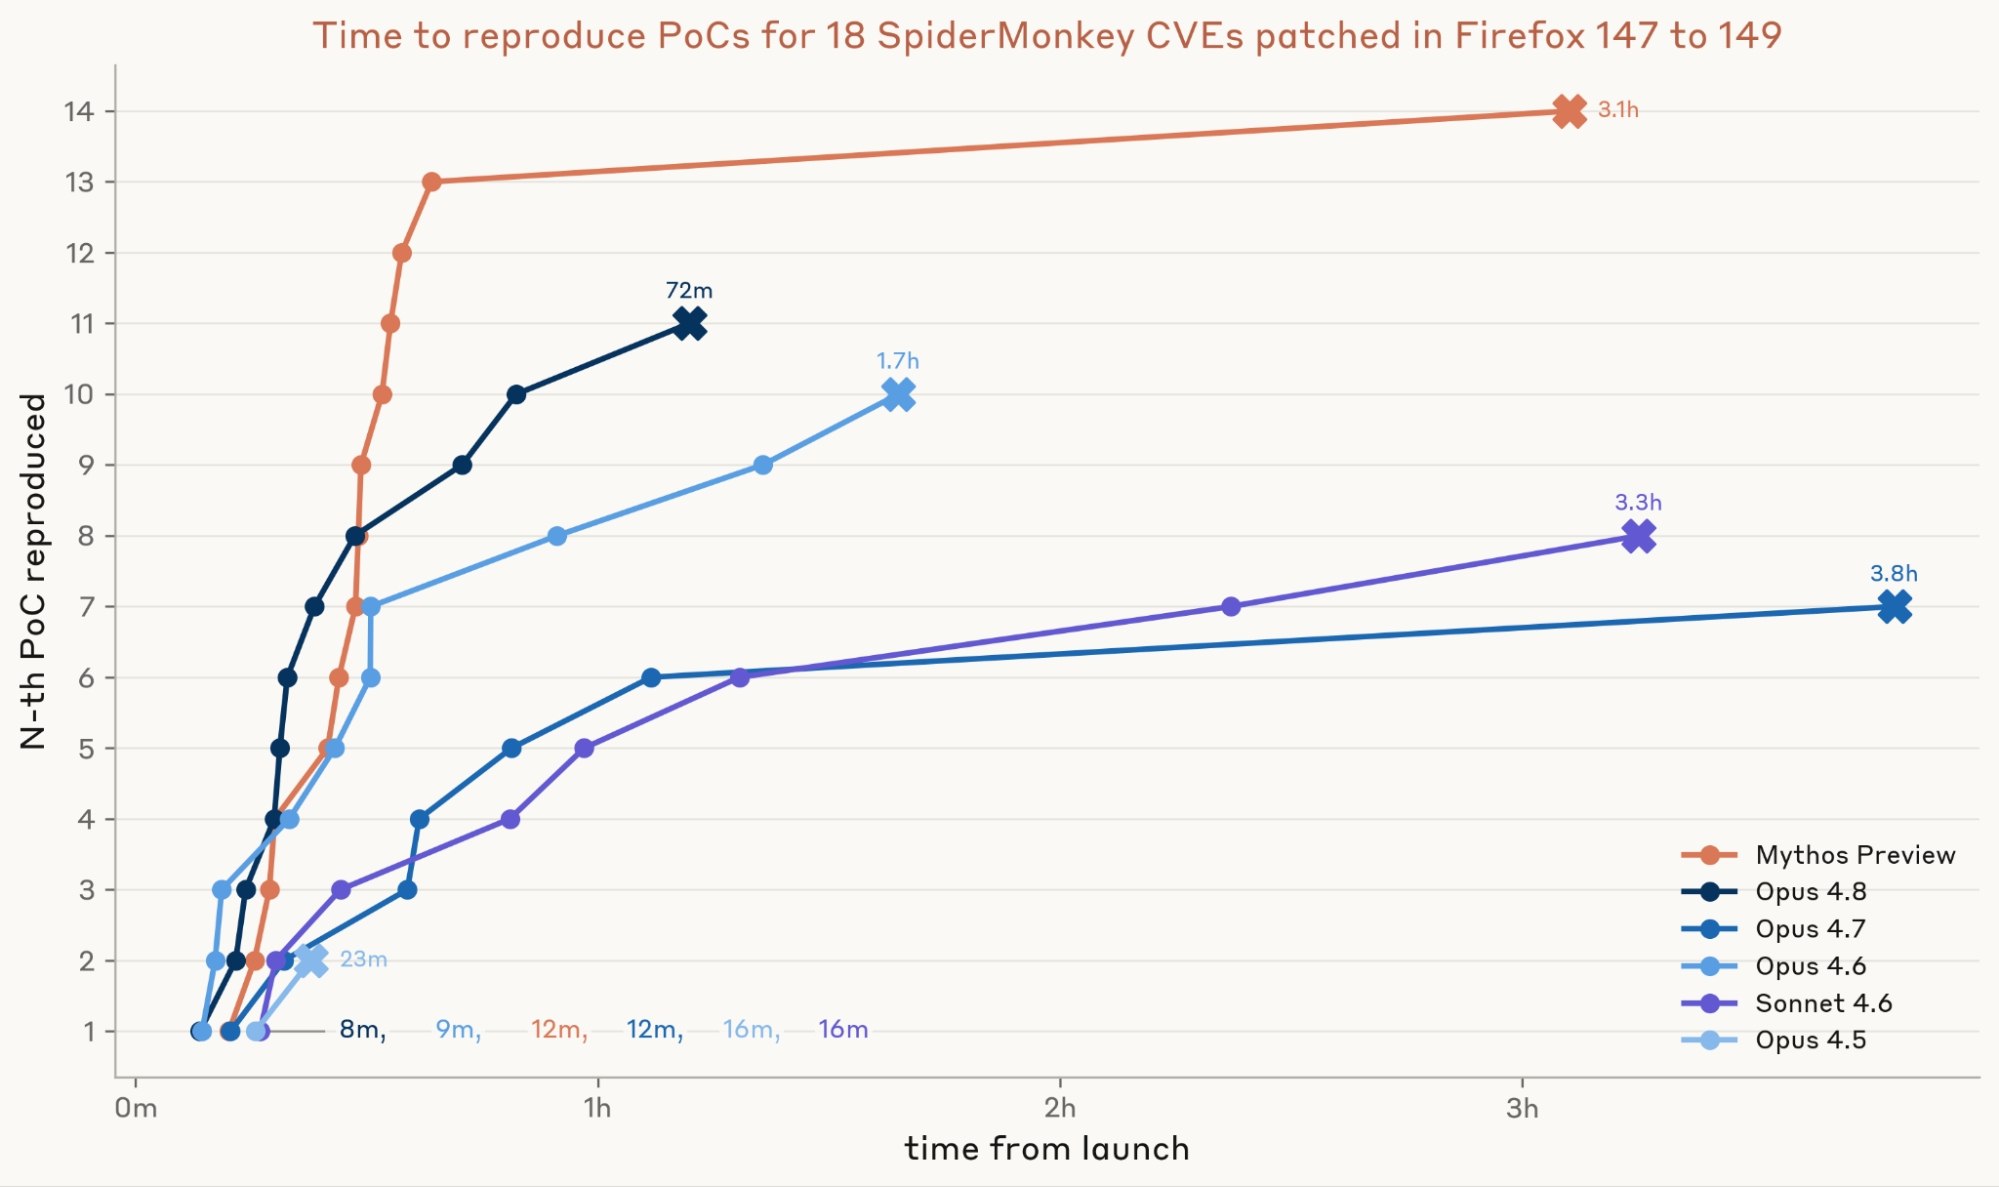
Anthropic’s Mythos Preview model can turn a security patch into a working exploit in hours. Tests on Firefox and Windows show the model autonomously finds vulnerabilities faster than companies can distribute updates.
Related stories
- Claude Code’s sandbox ships as an open-source npm package
- Claude Code stores MCP OAuth tokens in plaintext on Linux
- Vulnerabilities in Claude Code plugin marketplace
- Agentjacking vulnerability exposes Claude Code and Cursor to hijacking via fake error reports
- Apiiro finds Claude Code secrets in 1,122 GitHub files
- Email leak stopgap in Claude Code checks only shell calls
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.