
Anthropic tests AI exploit development speed
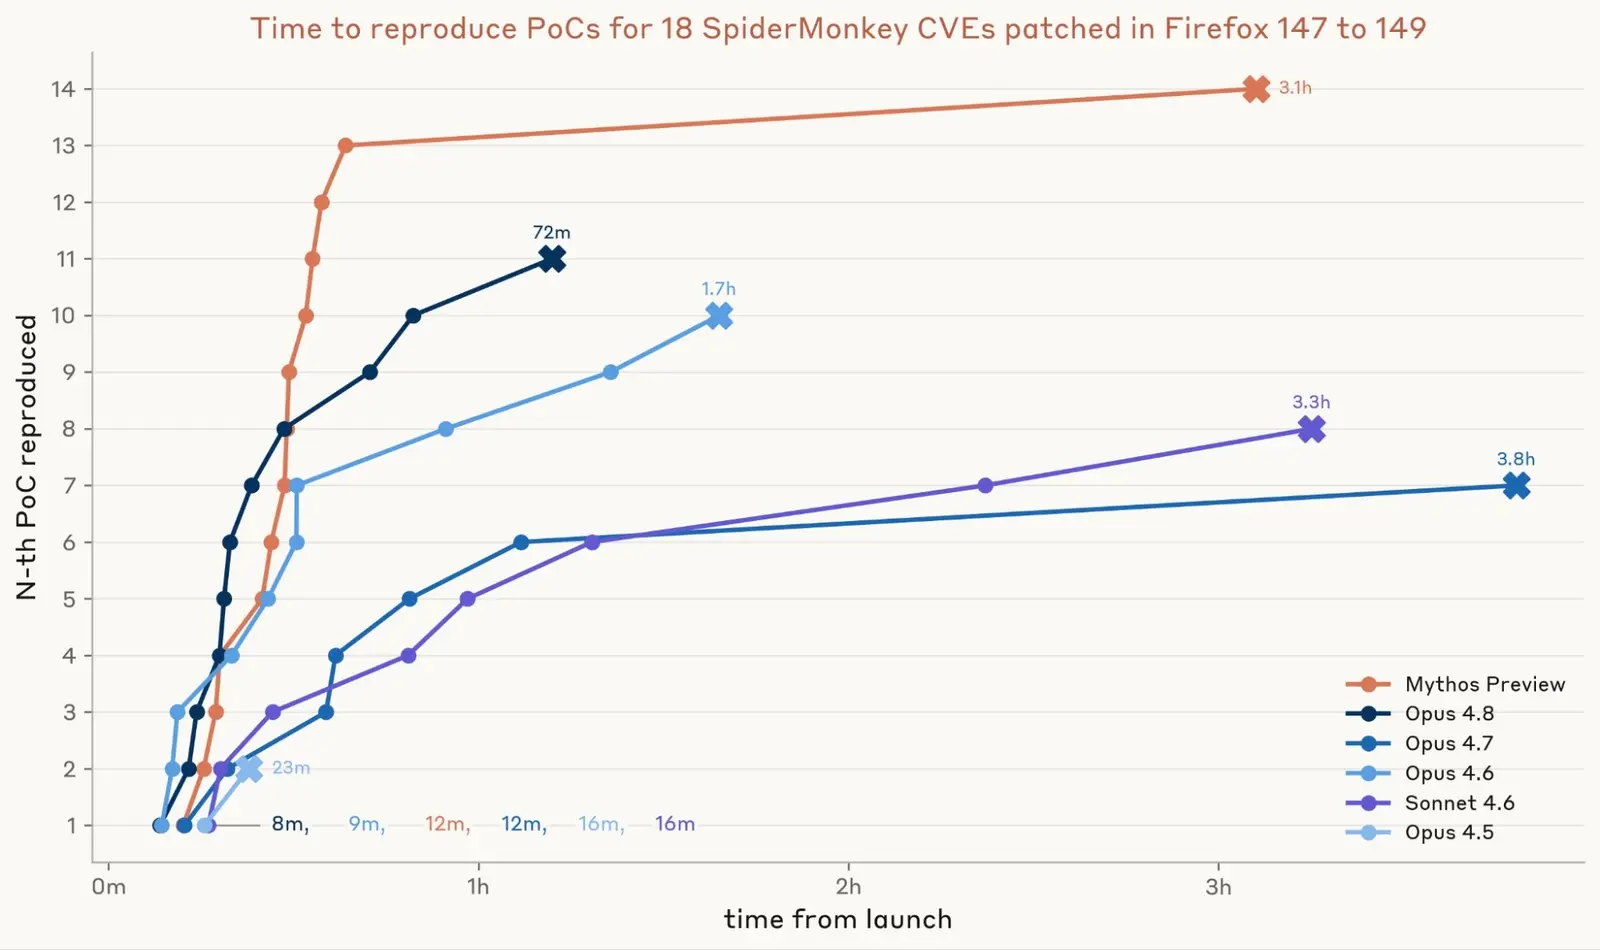
Researchers at Anthropic evaluated how models automate N-day exploit development - vulnerabilities with patches out but systems unupdated. In tests, the Mythos Preview model created working exploits for 8 of 18 Firefox vulnerabilities and 8 privilege-escalation chains to SYSTEM on Windows.
For Firefox, the model generated PoCs in 12-40 minutes and full exploits in 12 hours. On Windows, where source code isn’t available, it crafted exploit chains in 6 hours at around $2000 in API costs per case.
The authors note current patch cycles taking weeks no longer ensure protection. Models shrink exploit development from weeks of expert work to a few hours.
Up next
Vulnerability in Claude Dynamic Workflows access controls
Critical security update for Claude Code Dynamic Workflows. Subagents can bypass access controls and run commands with elevated privileges, ignoring sandbox settings. Admins are advised to forcibly disable Workflows until the bug is fixed.
Related stories
- Alberta government scans 466 million lines of code with Claude
- FlashProve proofs cost ~70-95x the GPU time of inference
- A Claude sandbox memory dump yielded a valid Google token
- Claude model wrote a no-login Linux root exploit
- Claude grades its own chats for misuse, catching 78%
- Unreleased Claude model built a one-click Chrome exploit
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.