
Critical vulnerability disclosures surge following Claude Mythos Preview
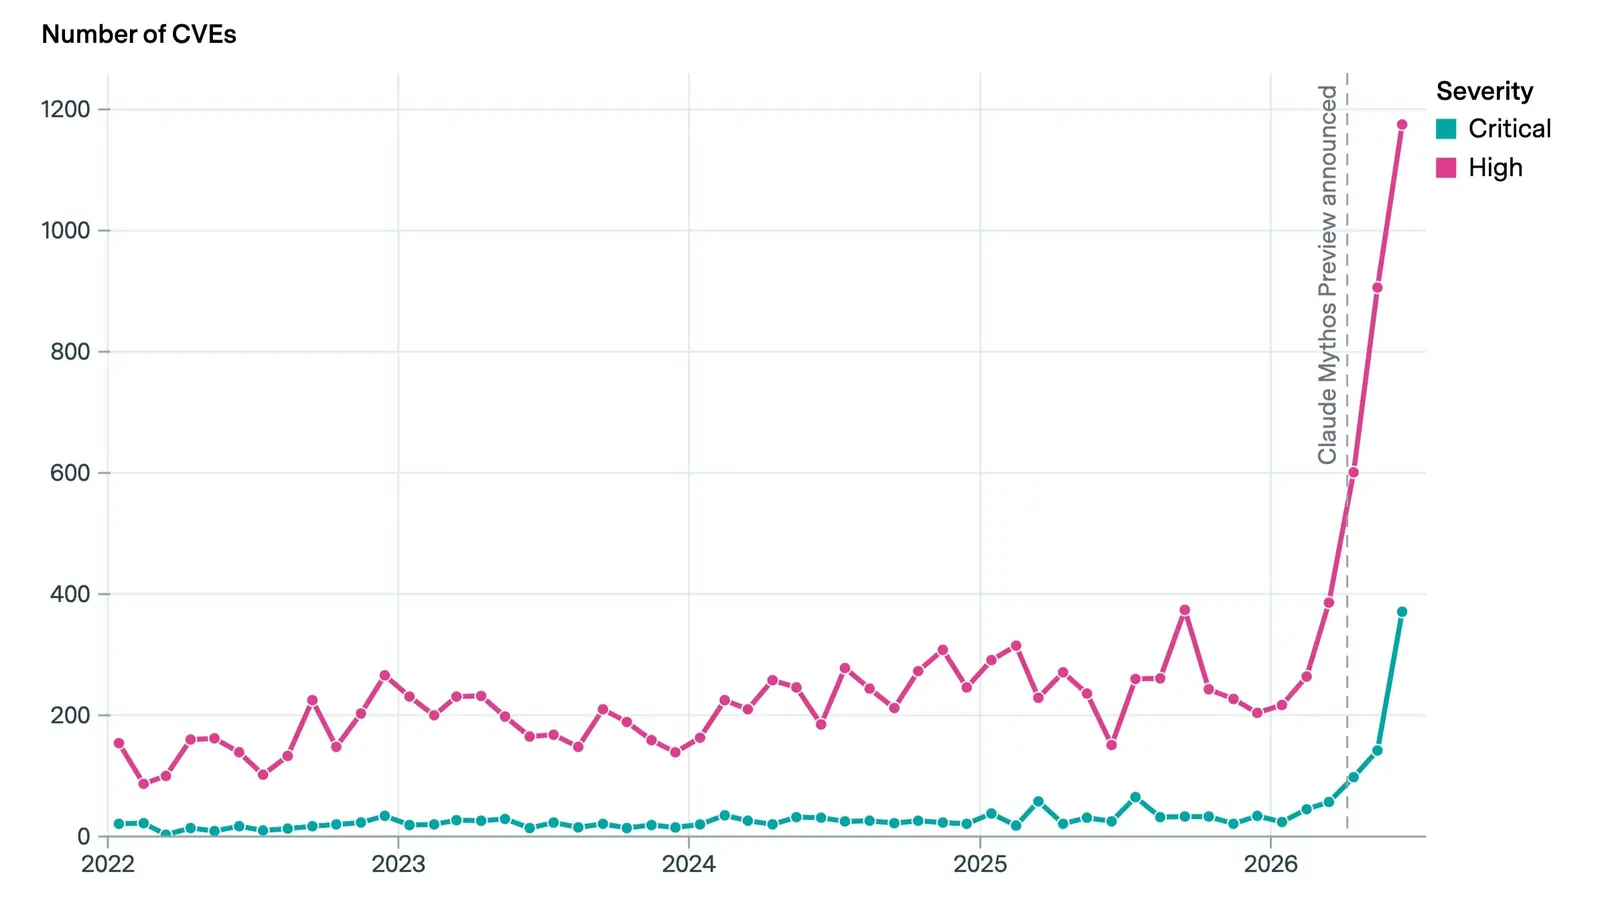
The number of disclosed high-severity vulnerabilities (CVEs) spiked in 2026. In June, 21 major organizations published approximately 1,500 high and critical vulnerabilities, a figure more than 3.5 times higher than the previous monthly record set before the Mythos release.
The increase follows Anthropic’s April announcement that Claude Mythos Preview can autonomously identify software vulnerabilities. Partners in Project Glasswing, including Microsoft, Google, Apple, and AWS, utilized the model to find and patch bugs prior to public disclosure.
Since the inception of Project Glasswing, the initiative has identified over 10,000 high and critical vulnerabilities, many of which remain undisclosed individually. OpenAI conducts similar work through its Daybreak product. Epoch published the CVE data under a Creative Commons BY license.
Up next
FleetView: a browser-based dashboard for parallel Claude Code agents
FleetView renders a grid of live terminals in your browser, each running a Claude Code instance. When an agent needs you, its window highlights and triggers an alert. It uses unique FLEET_PANE_ID assignments and Claude Code hooks to signal attention, avoiding the need for text parsing. It runs on tmux, so your sessions persist through restarts.
Related stories
- Anthropic says Claude found weaknesses in HAWK and AES
- US government lifts restrictions on Anthropic’s Mythos 5
- Apiiro finds Claude Code secrets in 1,122 GitHub files
- Email leak stopgap in Claude Code checks only shell calls
- Claude Code agent sat on a Pentagon network for two months
- Irregular CEO blames human error for AI agent breaches
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.