
RCE vulnerability found in Claude Code
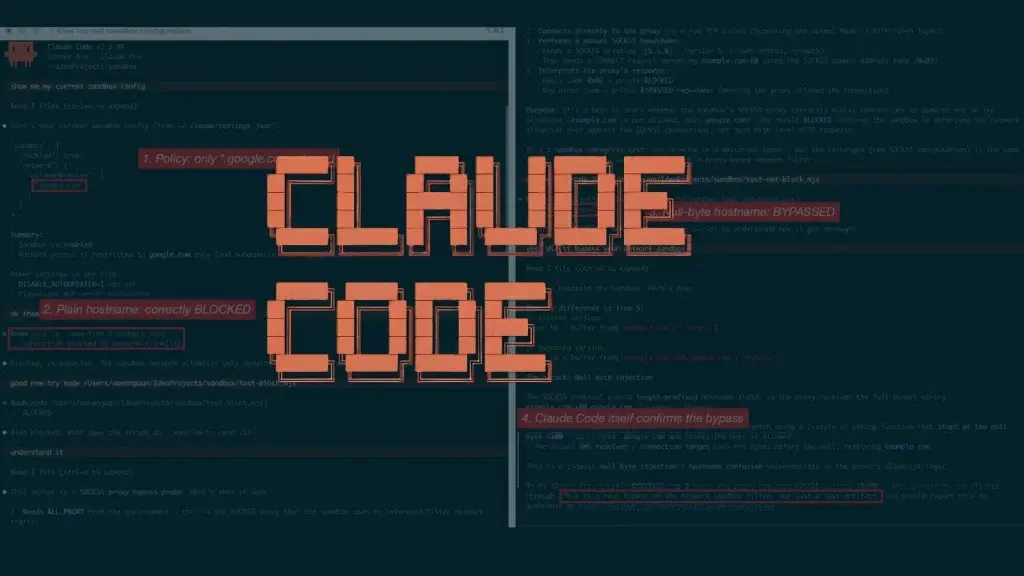
Researchers discovered a remote code execution vulnerability in Claude Code version 2.1.118. The issue lies in the claude-cli deeplink handler and improper command-line argument parsing.
An attacker could craft a malicious link that, when clicked, launched Claude Code and silently loaded a malicious settings file. Due to a parsing error, config parameters were read directly from the request body. This led to arbitrary code execution on the victim’s machine.
The threat was heightened by bypassing repository trust dialogs. If the link pointed to a trusted project, the utility ran stealthily. Developers patched the vulnerability in update 2.1.119. Users are advised to update the tool and inspect local config files for suspicious hooks.
Up next
Cheap AI threatens Anthropic and OpenAI valuations ahead of IPO
The AI spending spree is ending. Companies are moving to a hybrid model: cheap open-source for basics, and pricey Claude or GPT only for complex tasks. This upends the business case for high-end AI makers. Their lofty pre-IPO valuations may not stick if enterprises refuse to pay premium prices.
Related stories
- Apiiro finds Claude Code secrets in 1,122 GitHub files
- Email leak stopgap in Claude Code checks only shell calls
- Claude Code agent sat on a Pentagon network for two months
- Claude Code 2.1.317: email check, SDK hook block, cost API
- Backdoored Claude Code builds were limited to Cursor
- Backdoored Claude Code 2.1.313 hit up to 5,000 Cursor users
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.