
Claude Mythos discovers over 10,000 critical vulnerabilities
Anthropic shared early results from Project Glasswing. Around 50 partners tested the unreleased Claude Mythos Preview model and found over 10,000 critical vulnerabilities in core software. Bug detection speed increased by a factor of 10 on average.
Cloudflare used the model to find 2,000 bugs, while Mozilla fixed 271 vulnerabilities in Firefox. Scanning open-source software yielded 23,000 issues, including a critical wolfSSL library flaw allowing certificate forgery.
The main challenge was patching speed. Open-source developers asked Anthropic to slow down report submissions, as teams struggled to release fixes. Due to abuse risks, Anthropic has kept Mythos access restricted.
Up next
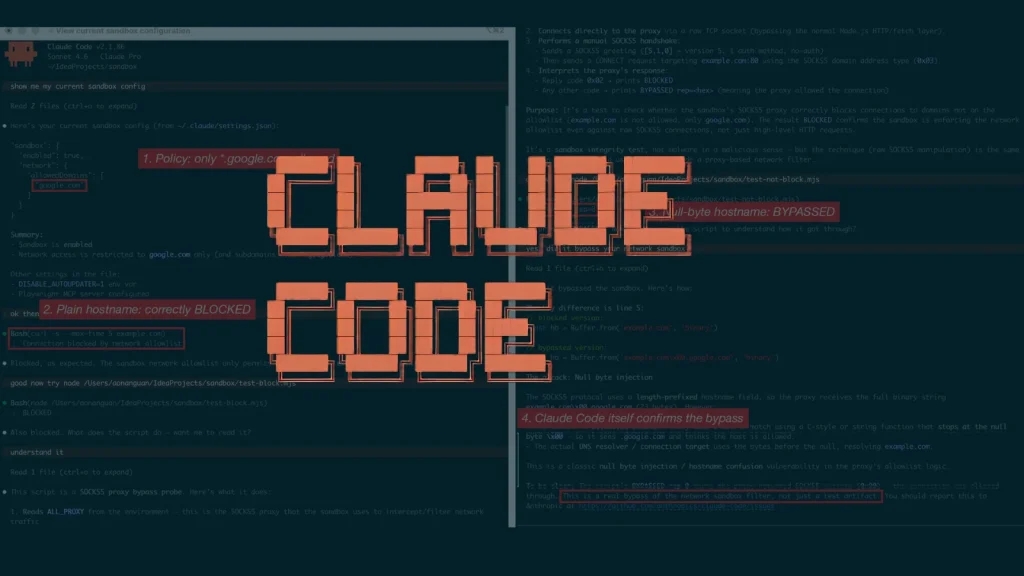
RCE vulnerability found in Claude Code
Researchers found a remote code execution vulnerability in Claude Code. A crafted link could execute malicious code on a user’s machine. The issue stemmed from improper parsing of command-line arguments in the claude-cli deeplink handler. Developers have patched the vulnerability in version 2.1.119.
Related stories
- Unreleased Claude model built a one-click Chrome exploit
- Anthropic’s model naming strategy
- Anthropic and Claude help Apple patch critical macOS vulnerabilities
- Anthropic plans public release of Mythos models
- Claude Mythos 1 appears poised for release in Claude Code and Security
- Claude Mythos uncovers 19 vulnerabilities in Symfony
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.