
Anthropic’s Mythos helps discover macOS vulnerabilities
Researchers at Calif used Anthropic’s unreleased Mythos model to find two previously unknown security holes in Apple’s macOS. These bugs allowed for privilege escalation and memory protection bypass. The Calif team chained them into an exploit sequence capable of giving full device control.
A 55-page report has been sent to Apple, which confirmed receipt and is reviewing the findings. This is the first time a major OS vendor has received a vulnerability report generated with Mythos’ help. Previously, the model found critical errors in OpenBSD and Linux.
Calif’s CEO, Tai Duong, emphasized that AI alone was not enough. Mythos accelerates the search, but human expertise is still required to craft a working exploit. Anthropic keeps the model under wraps through Project Glasswing, citing risks to global infrastructure. We previously reported on Mythos helping the US banking sector uncover hidden threats in their systems.
Up next
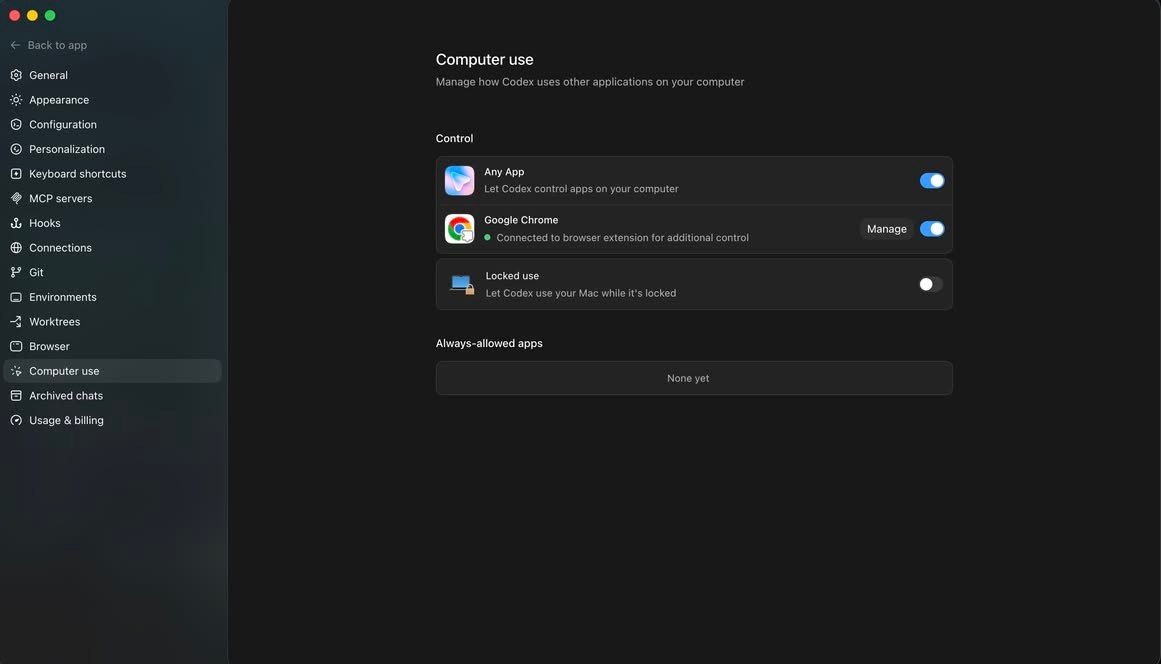
OpenAI tests Codex on locked Macs
OpenAI is testing a feature that lets Codex run on Macs even after the screen is locked. This turns the AI from a simple helper into a background operator that can perform tasks without human involvement. The line between active computer use and autonomous agent work is blurring.
Related stories
- Claude Mythos discovers over 10,000 critical vulnerabilities
- Claude Mythos uncovers 19 vulnerabilities in Symfony
- Anthropic restricts access to Claude Mythos for EU countries
- FlashProve proofs cost ~70-95x the GPU time of inference
- A Claude sandbox memory dump yielded a valid Google token
- Claude model wrote a no-login Linux root exploit
Comments
No comments yet. Be the first.
Join the conversation
Sign in to leave a comment. It appears after moderation.